Phishing-Proof MFA That Stops Social Engineering

Microsoft’s recent advisory on Octo Tempest should make every CISO lose sleep. This group isn’t just hacking software vulnerabilities. They’re hacking people, impersonating employees, tricking help desks into resetting passwords, stealing session cookies, and bypassing legacy MFA with social engineering.

Kevin Surace
1 minute read

AI-Generated Phishing Attacks Are Making Legacy MFA Obsolete

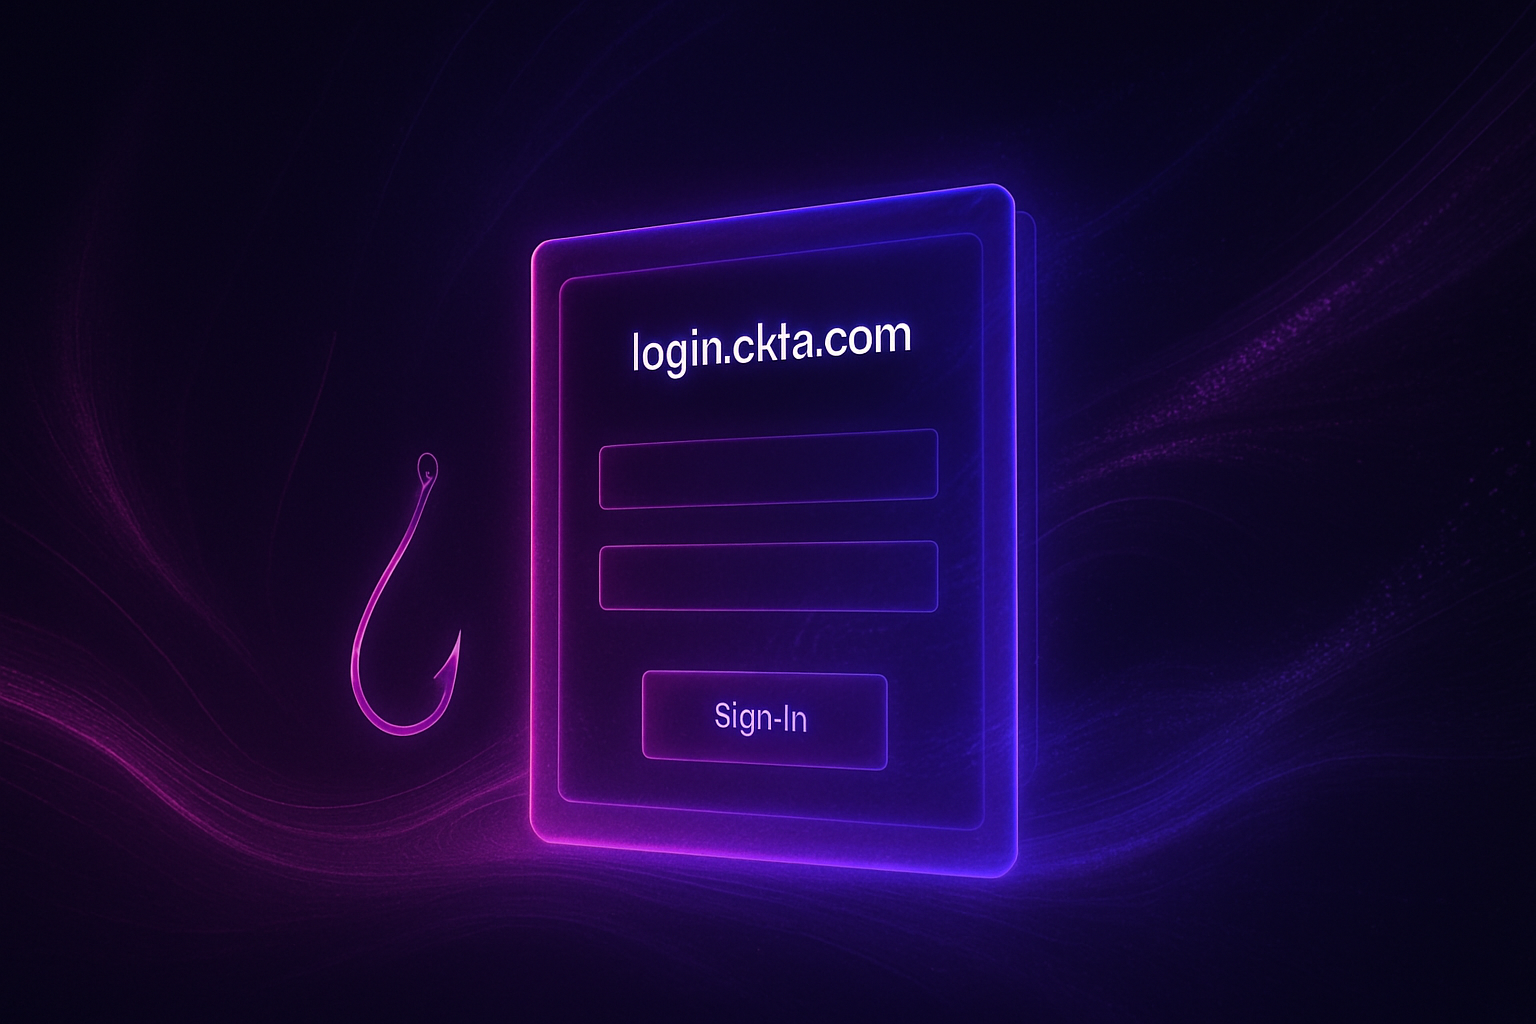
Generative AI just made phishing so easy that anyone can do it—and do it convincingly. According to Axios, researchers demonstrated that in just 30 seconds, a simple natural-language prompt was all it took to build a pixel-perfect spoofed login site. No coding. No technical skills. Just type “build a copy of the website login.okta.com,” and a convincing clone appears, ready to trick anyone into handing over credentials.

Kevin Surace
2 minute read
Stolen credentials are the new front door

Stolen Credentials Are the New Front Door

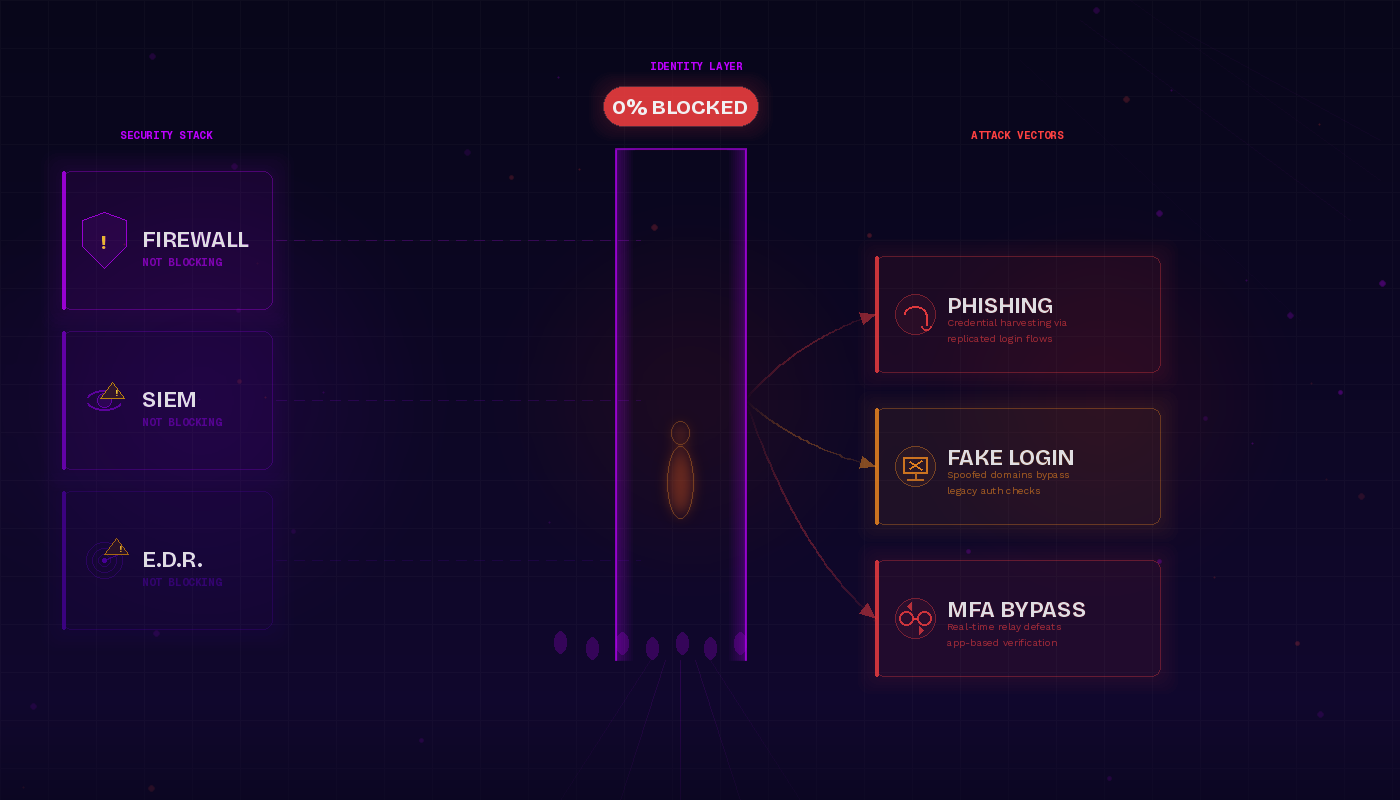
Attackers are not breaking in. They are logging in. Stolen credentials are now the most reliable entry point for enterprise breaches. Most defenses are built to stop an attacker trying to force their way through. The attacker who already has a valid username and password walks straight past them.

Kevin Surace
2 minute read
Scattered Spider is targeting Fortune 500 firms

Scattered Spider Hackers Are Hunting the Fortune 500

A new report from CyberCube just confirmed what many of us in cybersecurity have long suspected: Scattered Spider is targeting hundreds of major enterprises with precision. Nearly 300 companies—each with over $500 million in annual revenue—have been flagged as high-risk. Why? Because they’re still running the same legacy technologies this threat group exploits with shocking ease.

Kevin Surace
1 minute read
Scattered Spider 500+ domains

Scattered Spider's 500+ Phishing Domains and How to Stop Them

If your organization still relies on passwords, SMS codes, or authenticator apps to protect employee logins, it’s not a matter of if you’ll be breached—it’s when.

Kevin Surace
3 minute read
The MFA your trust is lying to you

The MFA You Trust Is Lying to You

As seen in Bleeping Computer

Kevin Surace
< 1 minute read
What are passkeys? Passkeys vs. Token

What Are Passkeys and Where They Fall Short

Passkeys are a genuine step forward from passwords. They use cryptographic key pairs instead of credentials you type and remember. The private key never leaves your device. The site you are logging into never sees it. There is nothing to phish, nothing to guess and nothing to leak in a breach. That matters. Most data breaches start with stolen or weak credentials. Passkeys remove that attack surface. But passkeys are not a complete solution for enterprise security. Several specific scenarios leave organizations exposed. This guide explains how passkeys work, where they are genuinely strong and where the gaps are.

Kevin Surace
4 minute read
Ingram Micro Down. Ransomed.

The Ingram Micro Ransomware Attack and the Legacy MFA Failure

Token Would Have Stopped This Cold. Another week, another breach. This time it’s Ingram Micro, one of the largest tech distributors on the planet. Systems down for days. Operations halted. Now they’re staring down a ransomware demand, possibly for millions.

Kevin Surace
2 minute read
Amazon's email to customers

Why Amazon's Phishing Email Warning Falls Short

Amazon just sent out a warning about phishing emails targeting Prime members—scammers spoofing login pages and tricking users into handing over their credentials. Sound familiar?

Kevin Surace
1 minute read
Qantas breach could have been avoided

The Qantas Data Breach: Weak MFA and Social Engineering

Last week, Qantas joined a growing list of high-profile companies breached by Scattered Spider, a sophisticated threat group known for exploiting human error and weak authentication systems—not by hacking through firewalls, but by walking right through the front door.

Kevin Surace
2 minute read
Hawaiian Airlines Attack Echoes Aflac, Underscores Need for Phishing-Proof MFA

The Hawaiian Airlines Data Breach and the Legacy MFA Failure

When Hawaiian Airlines confirmed a recent cyberattack that disrupted its internal systems, it wasn’t just another headline—it was another red flag.

Kevin Surace
2 minute read
Aflac Breach

The Aflac Data Breach Shows Why Legacy MFA Is Broken

The Aflac breach last week wasn’t pulled off by elite hackers—it was enabled by the same outdated multi-factor authentication (MFA) most enterprises rely on today.

Kevin Surace
1 minute read

Stay Identity Assured

Subscribe to The Assured Identity Brief for sharp insights on identity security, authentication, and the threats security leaders must stay ahead of.