CMMC Phase 1

Prove the Person. Protect FCI and CUI.

Support CMMC Phase 1 with phishing-resistant MFA authentication

CMMC Phase 1 puts cybersecurity requirements directly into defense contracts for organizations handling Federal Contract Information and Controlled Unclassified Information. TokenCore™ delivers FIDO2-certified, hardware-bound authentication that proves the authorized person before access is granted, strengthening identification, authentication, access control, and audit evidence.

No shared secret. No code to phish. No fallback.

Masthead-2

The Rollout

Requirements in the Contract.

Understanding CMMC Phase 1

The Cybersecurity Maturity Model Certification program moves the Defense Industrial Base from stated compliance to proven compliance. Phase 1 is the point where it enters solicitations and contract awards.

Phase 1 Rollout

The first step of a phased rollout. CMMC requirements start appearing in new DoD solicitations and become a condition of award.

Effective Date

Phase 1 began November 10, 2025. CMMC requirements now appear in new DoD solicitations wherever the program office or requiring activity specifies a level, so readiness is a present obligation.

Level 1 (FCI)

Fifteen basic safeguarding requirements for organizations handling Federal Contract Information. Identification and authentication are among them.

Level 2 (CUI)

One hundred and ten requirements for organizations handling Controlled Unclassified Information. Multi-factor authentication is named outright.

Self-Assessment Requirements

Levels 1 and 2 begin with self-assessment and an annual affirmation by a senior official. The affirmation is signed, so the evidence behind it has to hold.

FAR 52.204-21 and NIST SP 800-171 Rev. 2

Level 1 draws from FAR 52.204-21. Level 2 draws from NIST SP 800-171 Rev. 2. Both land on the same question: who is accessing the system.

The Requirements

Every Level Starts with Identity.

What are the CMMC MFA requirements?

Authentication requirements scale with the data you hold. Level 1 covers Federal Contract Information. Level 2 covers Controlled Unclassified Information and names multi-factor authentication outright. Both start from the same point: the system has to know who is at the keyboard.

Level 1

Identity, at the Point of Access.

CMMC Level 1 MFA requirements

Level 1 requires that users are identified and authenticated before access, and that access is limited to what each person is authorized to do.

IA.L1-3.5.1

User Identification

Every user, process, and device identified before anything else happens.

  • Unique user identity
  • No shared accounts
  • Identity established at the endpoint
User Identification

IA.L1-3.5.2

User Authentication

Identity claimed is identity proven. A password proves possession of a string, nothing more.

  • Verification of claimed identity
  • Authentication before access
  • Proof tied to the individual
User Authentication

AC.L1-3.1.1 / AC.L1-3.1.2

Access Control

Access limited to authorized users and to the transactions those users are permitted to run.

  • Authorized users only
  • Permitted transactions and functions
  • Systems handling FCI
Access Control

AC.L1-3.1.20

Remote and External Connections

Connections to and use of external systems controlled, wherever the work is done.

  • External system connections
  • Remote access protection
  • Same standard off site
Remote and External Connections

Level 2

Multi-Factor. Replay-Resistant.

CMMC Level 2 MFA requirements

Level 2 draws its authentication practices from NIST SP 800-171 Rev. 2. Multi-factor authentication is required, and a captured authentication cannot be replayed.

IA.L2-3.5.3

Multi-Factor Authentication

Multi-factor authentication for local and network access to privileged accounts, and for network access to every account.

  • Privileged accounts
  • Network access
  • Possession and inherence
Multi-Factor Authentication

IA.L2-3.5.4

Replay-Resistant Authentication

A captured authentication cannot be replayed. Codes can be replayed. Cryptographic challenges cannot.

  • Replay resistance for network access
  • Origin-bound credentials
  • Nothing reusable in transit
Replay-Resistant Authentication

IA.L2-3.5.10

Passwordless Authentication

Stored and transmitted passwords have to be cryptographically protected. Every password removed from the authentication path is one less credential in scope for this control.

  • No stored password to protect
  • No secret in transit
  • Credential held in the secure element
Passwordless Authentication

AU.L2-3.3.1 / AU.L2-3.3.2

Audit Logging

Audit records that trace actions back to the individual user who performed them.

  • Audit record creation and retention
  • Traceability to a single user
  • Evidence for assessors
Audit Logging

AC.L2-3.1.12 / AC.L2-3.1.13

Remote Access and Least Privilege

Remote sessions monitored and controlled, protected by cryptographic mechanisms, and held to the privilege each person actually needs.

  • Monitored remote sessions
  • Cryptographic protection of remote access
  • Privilege bound to a verified individual
Remote access session protected by hardware-bound multi-factor authentication
CMMC Phase 1 Requirements Mapping Guide Cover

The Guide

Map Every Requirement.

Download the CMMC Phase 1 Requirements Mapping Guide

The mapping guide lines up CMMC Phase 1 authentication requirements against phishing-resistant FIDO2 authentication, practice by practice. Mappings cover FAR 52.204-21, NIST SP 800-171 Rev. 2, identification and authentication, access control, audit and accountability, remote access, and passwordless authentication. A practical reference for teams preparing a self-assessment.

The Support

One Standard. Every Control.

How TokenCore supports CMMC authentication controls

Identification & Authentication

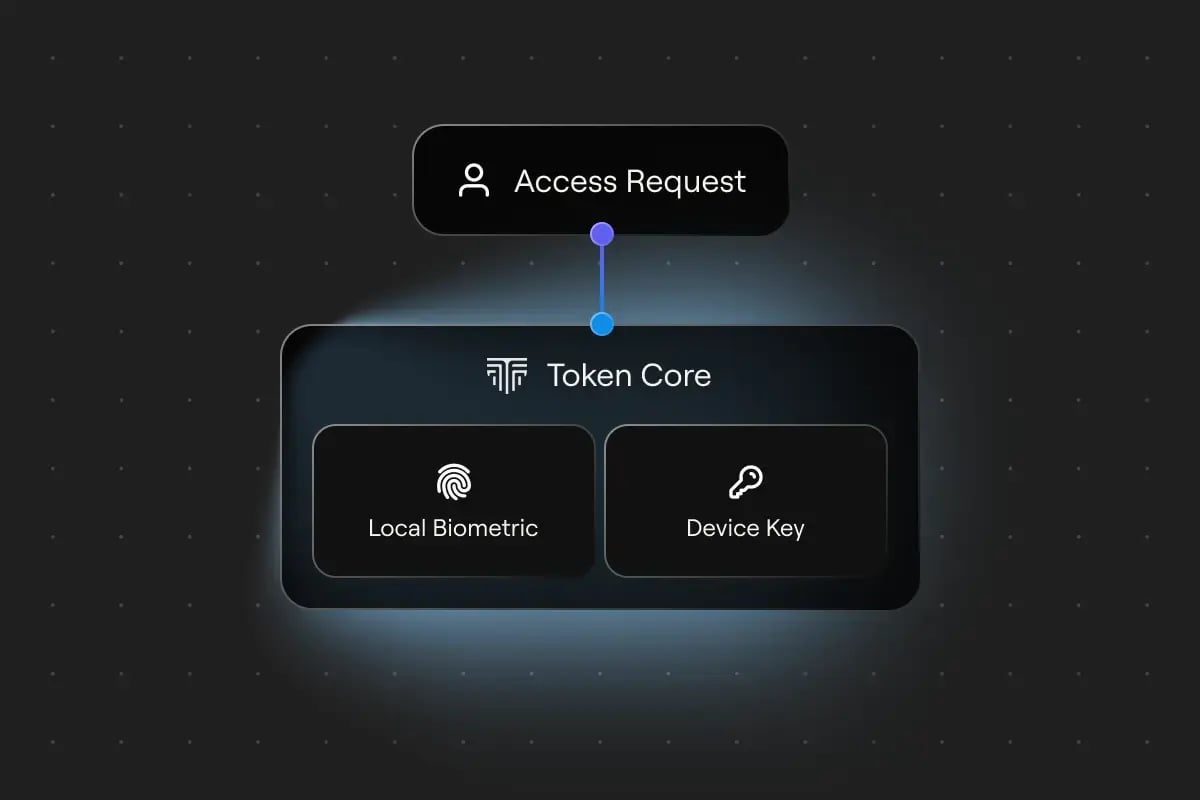
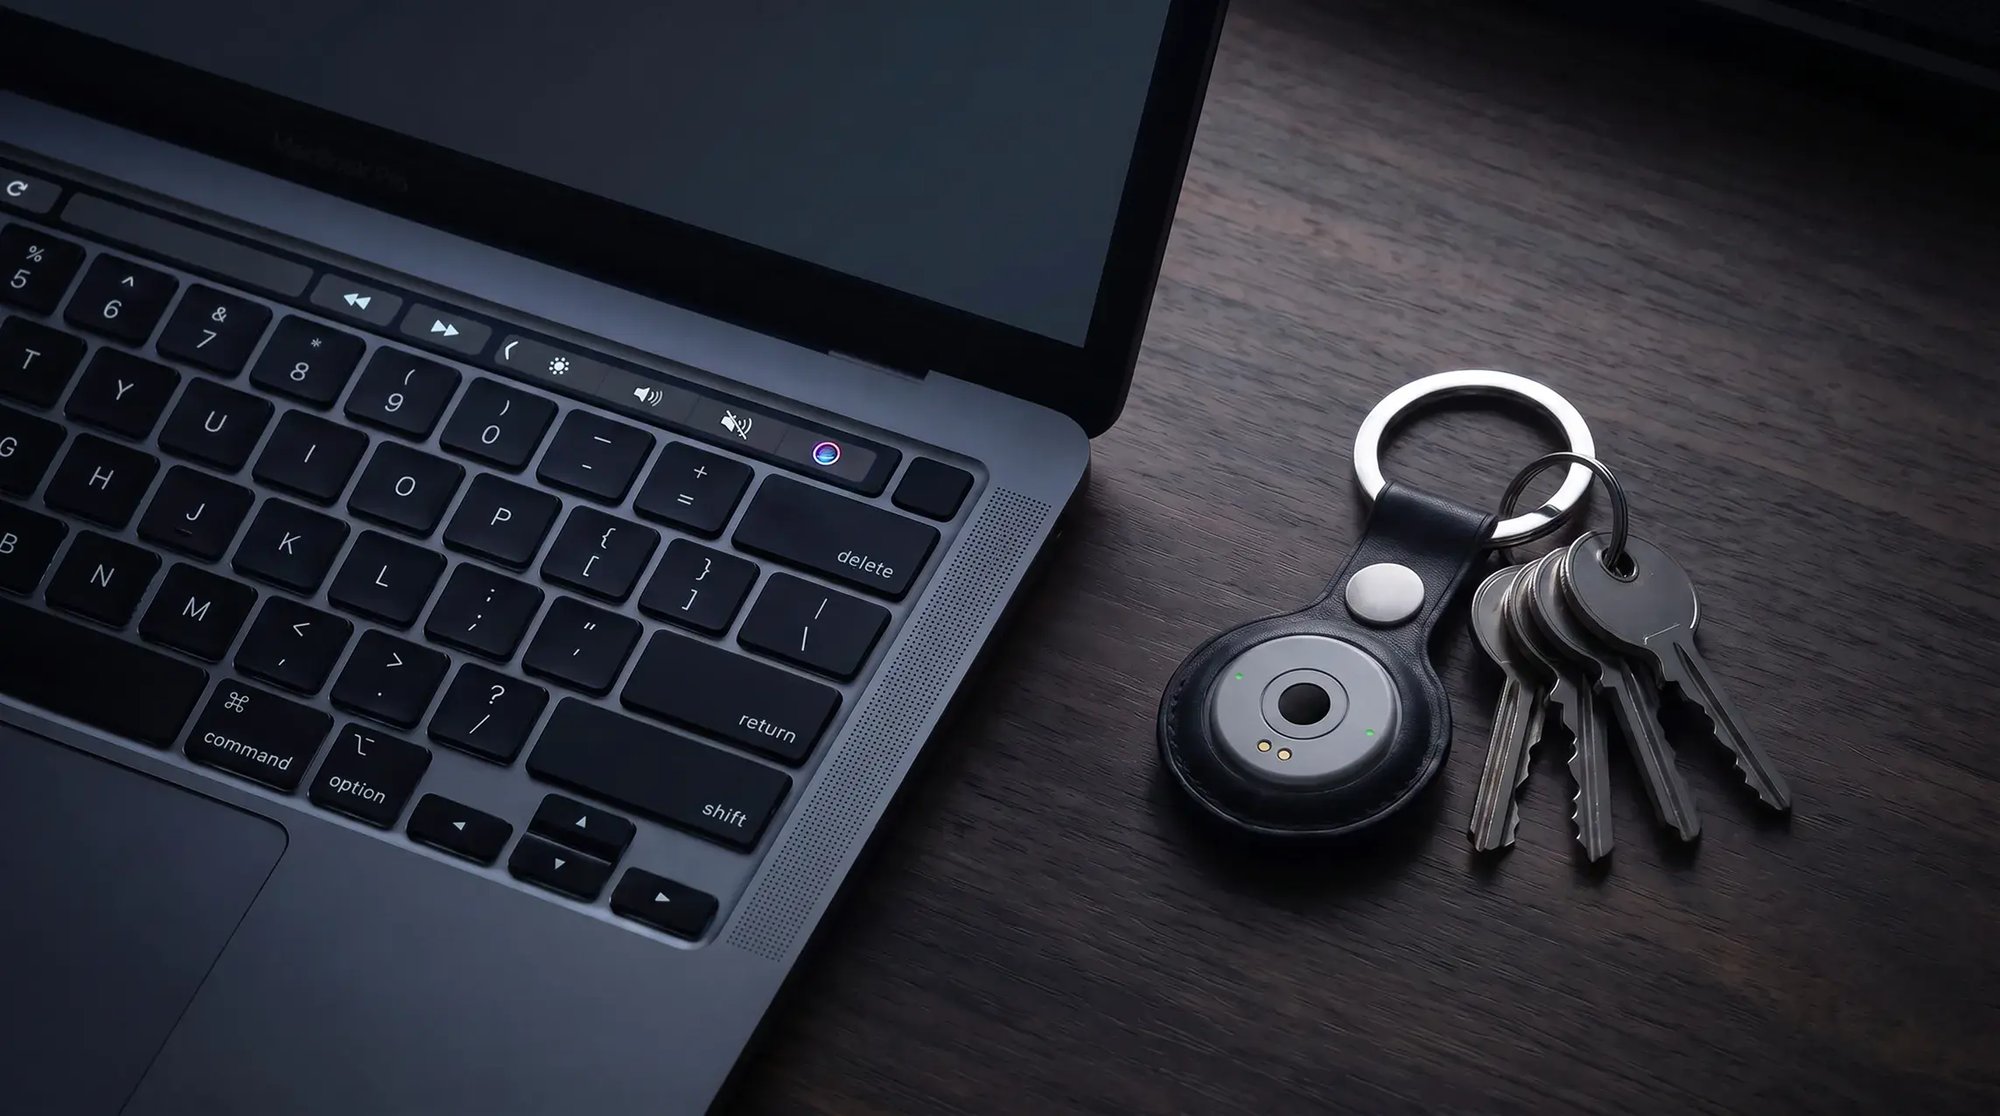
A fingerprint is matched on the hardware. The credential never leaves the secure element, and it belongs to one person.

  • Hardware-bound identity
  • Unique user authentication
  • Biometric verification

Phishing-Resistant MFA

Possession and inherence in a single action, bound to the legitimate domain. There is nothing to type and nothing to hand over.

  • FIDO2 authentication
  • Possession plus inherence
  • Replay resistance

Access Control

Credentials tied to hardware the user carries, so privilege travels with the person and not with a session.

  • Device-bound credentials
  • Least privilege
  • Remote access protection

Audit & Accountability

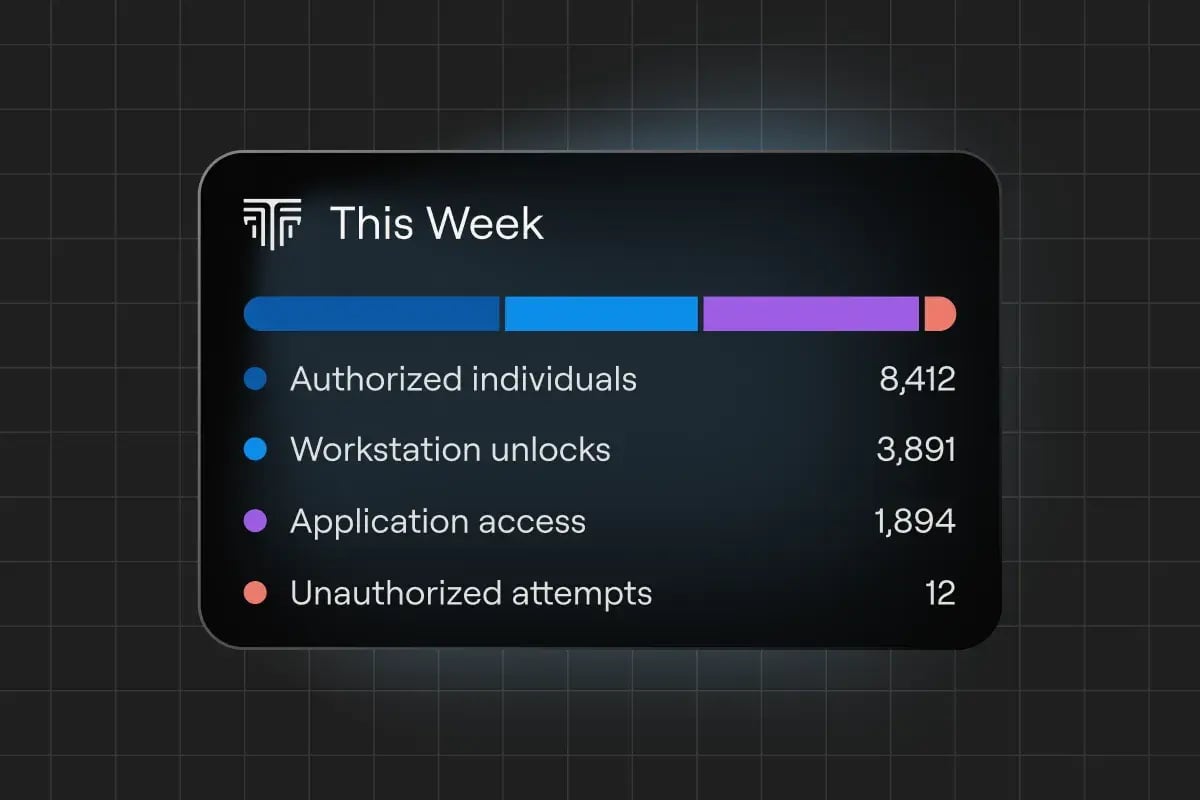
Every access event ties to a proven human, giving assessors a defensible record of who reached which system, and when.

  • Signed authentication events
  • Audit logging
  • Identity telemetry
  • Evidence for SPRS and POA&M

Supply Chain Security

DFARS obligations flow down the supply chain. External access is held to the same proven standard as internal access.

  • Subcontractors
  • MSPs
  • External service providers
  • DFARS flow-down obligations

Beyond Legacy MFA

The Code Is the Weakness.

Why defense contractors are moving beyond traditional MFA

The Risks of OTP Authentication

A one-time code is a shared secret, and a shared secret can be stolen. Intercept it and it still works. The code does not care who types it, which is what makes credential theft and replay attacks routine.

Push Fatigue & Help Desk Attacks

MFA fatigue wears approval prompts down until someone taps yes. Social engineering talks a help desk into a reset. Both end in credential compromise. TokenCore™ has nothing to approve and nothing to reissue.

Replay-Resistant Authentication

FIDO2 public key cryptography binds the credential to the hardware, the person, and the legitimate domain. Origin-bound means there is nothing to phish, nothing to reuse, and nothing to send.

Compatibility

Your Stack. Unchanged.

Built for existing defense identity infrastructure

TokenCore™ deploys alongside the identity and privileged access infrastructure you already run. It is a trust layer across your existing IAM stack, not a replacement for it.

Compatible with Leading Authentication Services

google-logo-white
okta-logo-white
oracle-logo-white
1password-logo-white
one-login-logo-white
cyberark-logo-white
google-logo-white
okta-logo-white
oracle-logo-white
1password-logo-white
one-login-logo-white
cyberark-logo-white

See It in Action

Make Identity Absolute

Strengthen authentication for CMMC Phase 1

See how TokenCore™ strengthens authentication controls for defense contractors, closes the credential-based attack path, and supports CMMC Phase 1 implementation with phishing-resistant FIDO2 authentication.