The DHS Breach Is A Warning to Every Okta Customer

The DHS Breach Is a Warning to Every Okta Customer

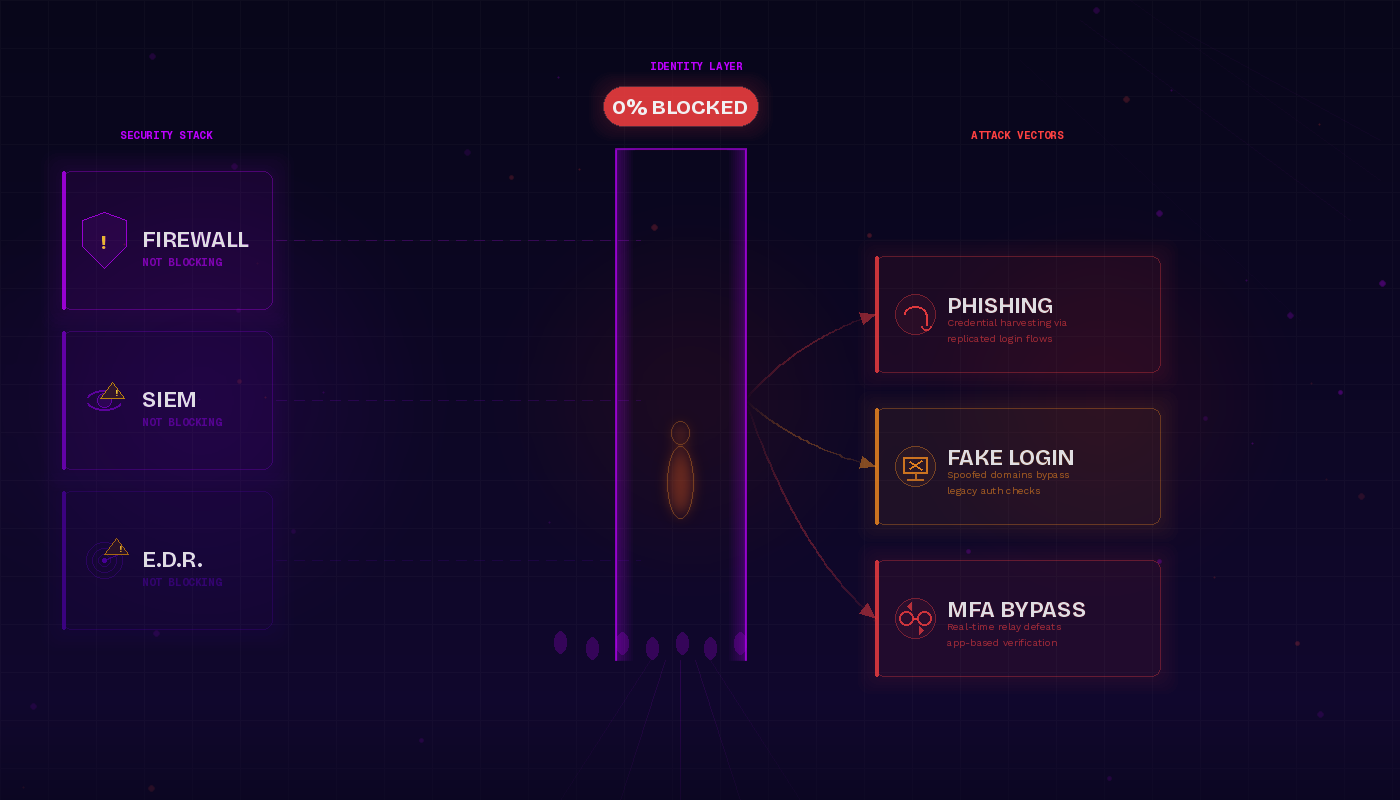
More than 40,000 Department of Homeland Security employee and contractor records have reportedly been exposed, including personnel from ICE, Customs and Border Protection, CISA and other sensitive agencies. And the most important part of this story may be how the attackers say they got access. Okta. According to reporting from Reuters and others, the group behind the breach claims the data was obtained through the Okta single sign on environment used by DHS personnel. DHS is investigating the breach. Okta says there is no evidence that Okta itself was compromised.

Kevin Surace
3 minute read

The Binance Hack: What If the Real Failure Was Identity?

The reported $6.3 billion Binance breach may become one of the most consequential cyberattacks ever. Early reporting points to a compromised DevOps engineer’s laptop and subsequent access to internal systems that enabled unauthorized transactions. But one critical question remains unanswered: How did the attackers gain trusted access in the first place?

Kevin Surace
2 minute read
Passkeys and Windows Hello Are No Longer Enough to Claim Phishing Resistance

Passkeys and Windows Hello Are No Longer Enough to Claim Phishing Resistance

For years, the cybersecurity industry has been moving toward what it calls phishing resistant authentication. Passkeys, Windows Hello, and FIDO2 have been central to that transition, and for good reason. They are a substantial improvement over passwords, SMS codes, and push based authenticator apps. But the phrase phishing resistant is now being stretched well beyond what it actually proves. The cryptographic protocol may resist a traditional fake website, while the complete authentication system around it remains vulnerable to malware, recovery attacks, endpoint compromise, cloud synchronization, social engineering, session theft, and enrollment abuse.

Kevin Surace
2 minute read
Your 15- or 30-Character Password Can Still Be Stolen From You in One Second

Your 15- or 30-Character Password Can Still Be Stolen From You in One Second

The latest password guidance sounds reassuring. Make passwords longer. Use at least 15 characters when a password is the only authentication factor. Screen passwords against known compromised credentials. Stop forcing people to change them every few months. Use password managers. All of that is sensible advice. It is also increasingly beside the point.

Kevin Surace
2 minute read
Google’s New Gemini Agent Platform Enables TokenCore Biometric Gates

Google’s New Gemini Agent Platform Enables TokenCore Biometric Gates

Google’s Gemini at Work 2026 announcements make one thing increasingly clear: as AI agents gain the ability to take real actions inside the enterprise, there have to be hard limits on what they can do autonomously. Gemini Enterprise is being built around Agent Identity, enterprise IAM, policy controls and Agent Gateway. Google now gives security teams the ability to govern which agents can reach particular resources, which tools they can invoke and whether certain actions are permitted. Importantly, those policies can explicitly distinguish destructive or irreversible actions from routine ones. That tells us something important: Google recognizes that agentic AI needs gates.

Kevin Surace
2 minute read

Scattered Spider Exploits the Weakest Passkey Door: Account Recovery

The Scattered Spider playbook starts with a phone call. As a recent Infosecurity Magazine article explains, attackers research an employee, call the help desk, and persuade someone to reset a password or replace an authentication factor by authorizing a new passkey on any device including a bad actors own phone. The business may have strong security at login, but the attacker never needs to defeat it. The attacker convinces the business to enroll their device instead. The FBI and its international partners have documented that pattern. Scattered Spider actors have persuaded support staff to transfer multifactor authentication to devices they control, then used those devices to enter single sign on environments. If an attacker can replace your authenticator through a convincing conversation, your strongest login method becomes optional.

Kevin Surace
3 minute read
Scattered Spider Is Not Beating MFA

Scattered Spider Is Not Beating MFA. It Is Beating the Reset Button.

For years, cybersecurity leaders have been told that multifactor authentication is the answer to stolen passwords. Deploy a second factor, train employees to recognize suspicious requests, monitor the network, and the organization will be safer. That advice was reasonable when attackers were primarily trying to guess passwords or deliver malware. It is far less effective against an adversary that understands a more uncomfortable truth: the easiest way around authentication is often to persuade an authorized person to replace it. That is the central lesson of Scattered Spider. The group is known for voice phishing, impersonation, and carefully researched calls to employees and help desk personnel. Its operators do not always need to discover a software vulnerability. They can call support, claim to be a stranded employee, and ask for a password reset or a new authentication factor. If the story is convincing and the recovery process is weak, the attacker receives legitimate access without ever defeating the technology protecting the original account.

Kevin Surace
4 minute read
Cyber Belongs in the Boardroom. So Does Identity.

Boards have accepted responsibility for cyber risk. Now they must focus on the place where so many breaches actually begin: identity. Kim Stewart Smith’s recent article makes an important argument. Cybersecurity and artificial intelligence are no longer operational IT concerns. They are governance issues. Boards are accountable for enterprise risk, and cyber now sits alongside financial, legal, regulatory, and operational risk as one of the most significant threats facing an organization. That is an important and overdue shift. But there is another question boards should now be asking. It is not simply whether cyber belongs in the boardroom. It is whether the board is spending enough time on the part of cyber that determines whether an attacker gets into the organization in the first place.

Kevin Surace
5 minute read
The Relay That Goes Nowhere

Adversary in the Middle Is Winning. Here’s How to Finally Shut the Door.

The team at Stingrai recently published one of the better explanations I’ve seen of Adversary in the Middle (AiTM) phishing attacks and why they’ve become one of the fastest-growing threats facing enterprises today. Their article explains not only how these attacks work, but why organizations that have already deployed multi factor authentication are still finding themselves compromised. It’s well worth reading because it highlights a difficult truth many security teams are just beginning to accept: successful authentication no longer means the right person logged in.

Kevin Surace
2 minute read
Indistinguishable pair

Phishing Doesn’t Look Fake Anymore. That’s Why Legacy MFA Is Finished.

For years, cybersecurity awareness training taught employees to recognize phishing by looking for obvious warning signs. Poor grammar, strange formatting, suspicious links, awkward branding and clumsy language were all supposed to help users separate legitimate communications from fraudulent ones. That model is rapidly becoming obsolete. As PCWorld recently pointed out, generative AI has fundamentally changed the quality of phishing. Attackers can now create emails that are polished, grammatically correct and extremely convincing. They can closely mimic the language, tone and structure of communications from Microsoft, banks, delivery companies and other trusted brands. The visual presentation has improved as well. In many cases, there is simply nothing obviously “fake” about the message anymore.

Kevin Surace
4 minute read
Infrastructure vs. identity

Another “Azure Breach”? Not Really. It Was Almost Certainly an Identity Breach.

Every few weeks another headline appears suggesting that a major cloud platform has been breached. This week, the alleged victims include household names such as McDonald’s, Vodafone, Kyndryl, Gap, Wyndham, and others, with millions of Azure and Entra directory records reportedly being offered for sale by a threat actor calling themselves “TheHatman.” But based on what has been reported so far, there is no indication that Microsoft Azure itself was compromised. The far more likely explanation is much simpler and much more important for enterprise security leaders to understand: someone obtained legitimate access and logged in.

Kevin Surace
4 minute read
The door that can't be opened from the outside

Apollo Wasn’t Hacked. They Were Authenticated.

Another major enterprise fell victim to identity-based social engineering. Here’s exactly how it happened, why legacy authentication failed, and why it’s time to rethink the front door. When Apollo Global Management recently disclosed a data breach, many headlines framed it as another sophisticated cyberattack. But if you look carefully at the publicly reported details, the story is actually much simpler. Attackers didn’t exploit an unknown software vulnerability. They didn’t bypass next generation firewalls. They didn’t crack encryption or deploy advanced malware. Instead, they convinced employees they were legitimate IT personnel, directed them to a convincing login page, and had those employees authenticate the attackers into Apollo’s own systems. The attackers didn’t break in. They logged in.

Kevin Surace
4 minute read
1 2 3 4 5 ... 7

Stay Identity Assured

Subscribe to The Assured Identity Brief for sharp insights on identity security, authentication, and the threats security leaders must stay ahead of.