FIDO2 + Fingerprint

Phishing-Resistant MFA Solutions

Phishing-resistant MFA has to stop what most MFA can't: codes relayed by fake sites and push prompts approved by mistake. TokenCore™ ties every login to the real website and needs your fingerprint on the device. Don't get trapped in spoofed domains.

login.acme-c0rp.com/sso

Sign in to Acme

Lookalike site

Emaildana@acme.com
Password ••••••••Captured
Domain check

Sign-in refused

  • Registered site login.acme.com
  • This page login.acme-c0rp.com
  • FIDO2 signature Not issued

Account protected. Nothing to relay.
Definition

What Makes MFA Phishing-Resistant

Phishing-resistant MFA is authentication that a fake website can't capture or replay. Three things make it so:

  • The login is bound to the real website's domain.
  • It uses public-key cryptography, so there's no shared secret to steal.
  • There's no code to type or prompt to approve.

CISA names FIDO2/WebAuthn and PKI-based smart cards as phishing-resistant. Read more on what phishing-resistant MFA is.

Challenge from login.acme.com

Signed on the device, for this domain only

  • Bound to the real domain Signed for login.acme.com, useless anywhere else
  • No shared secret Public key on the server, private key on the device
  • Nothing to type or approve No code to relay, no prompt to push
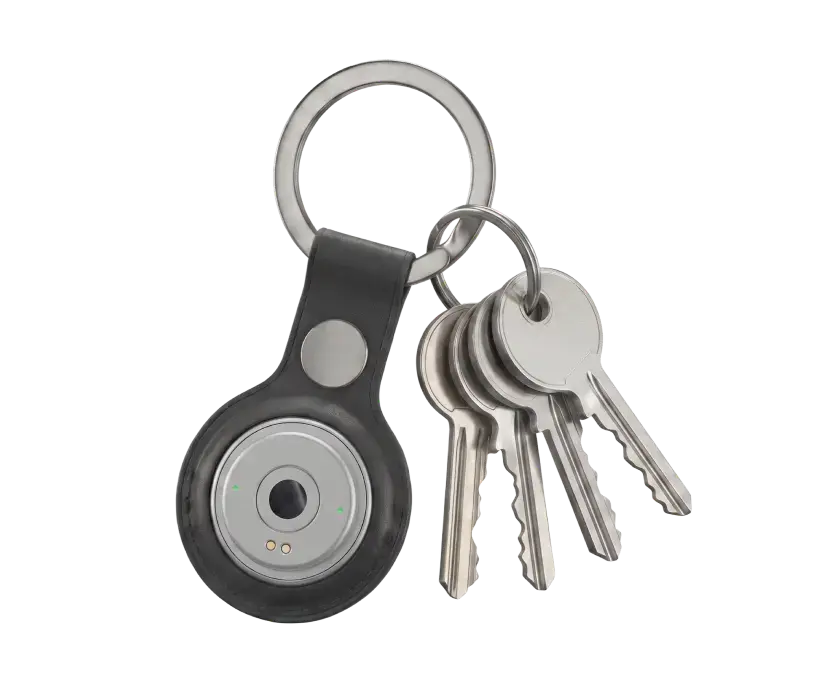
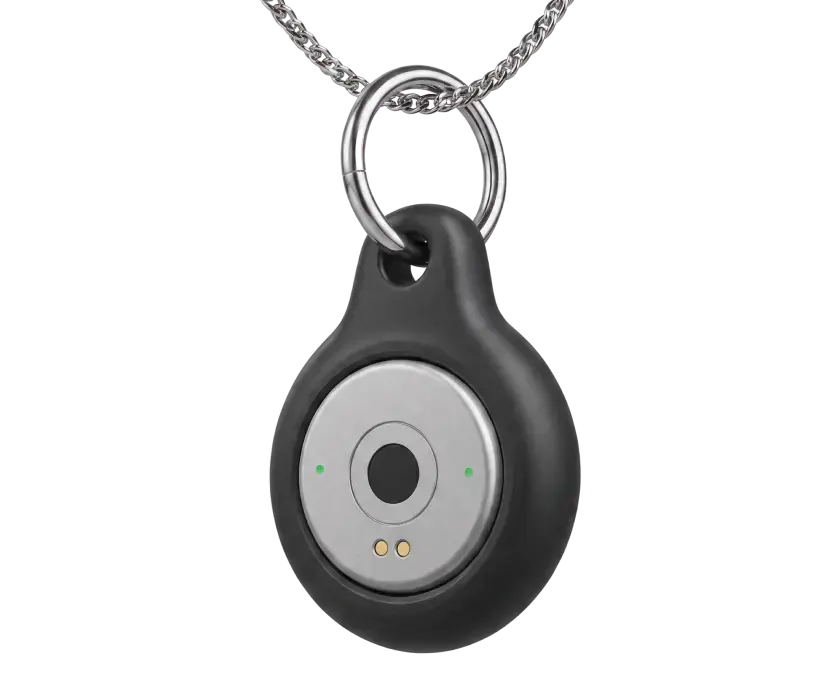
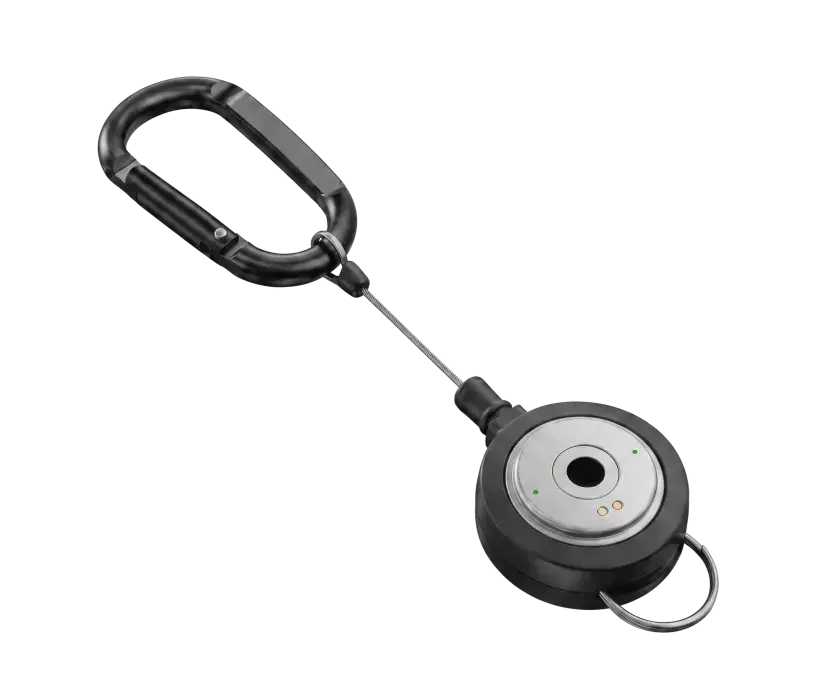
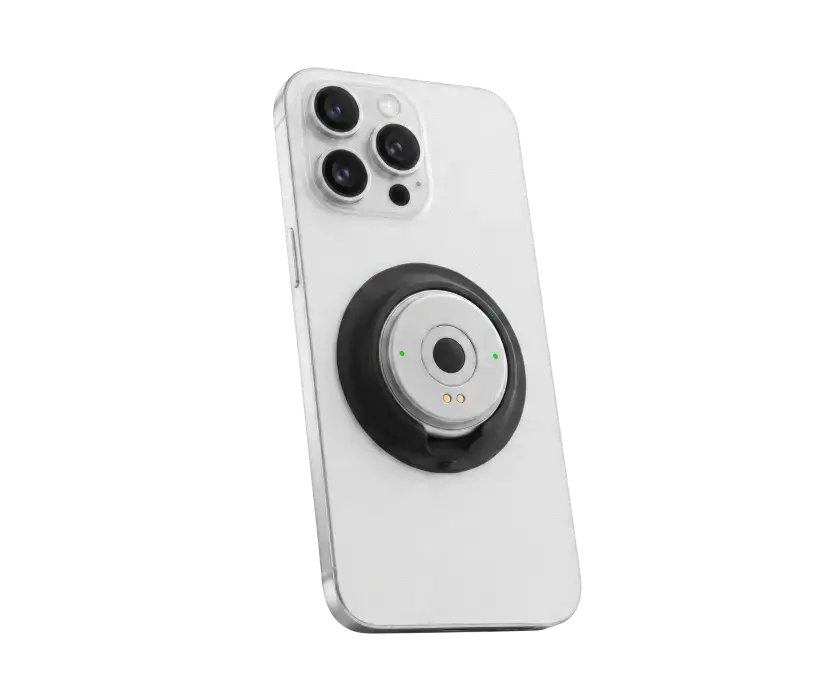
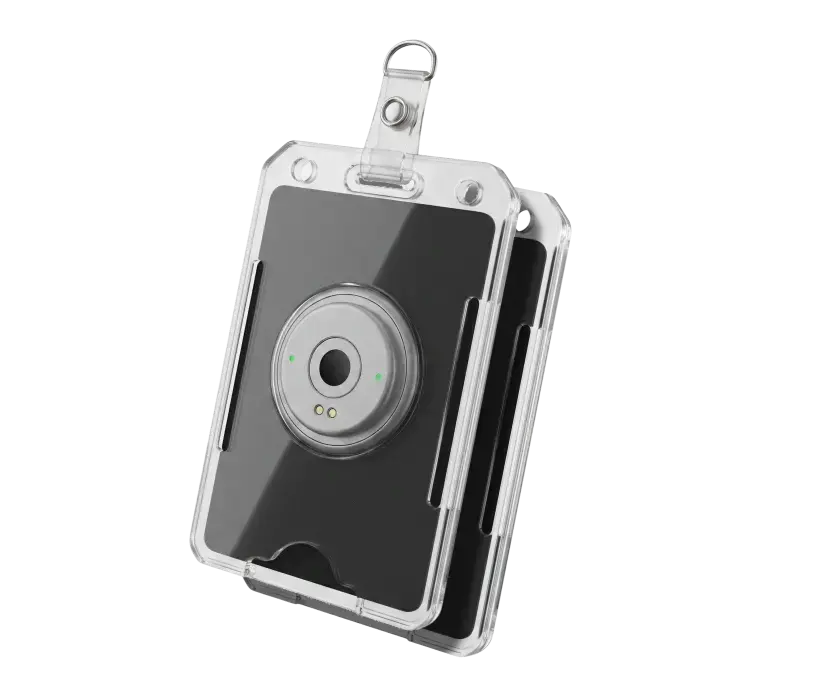
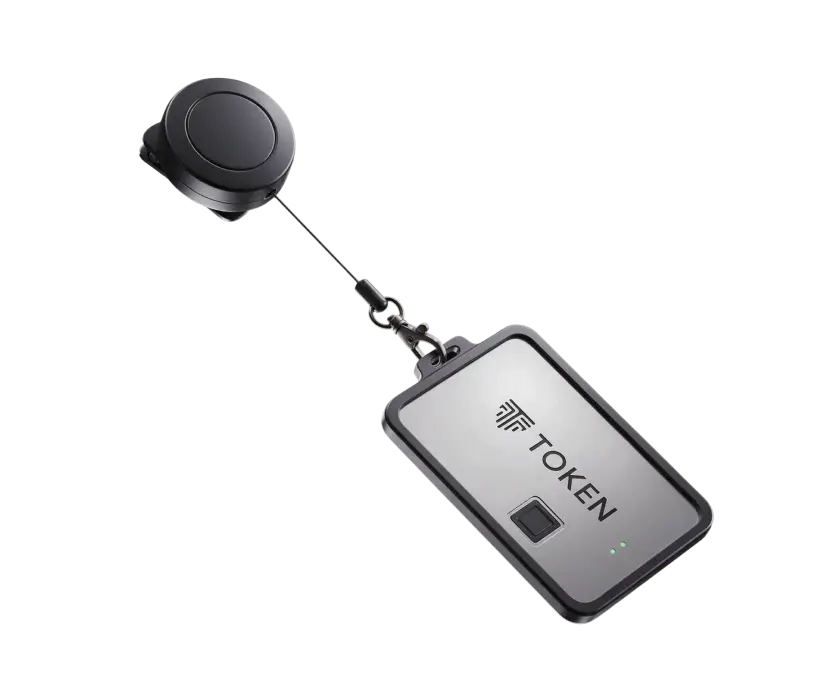
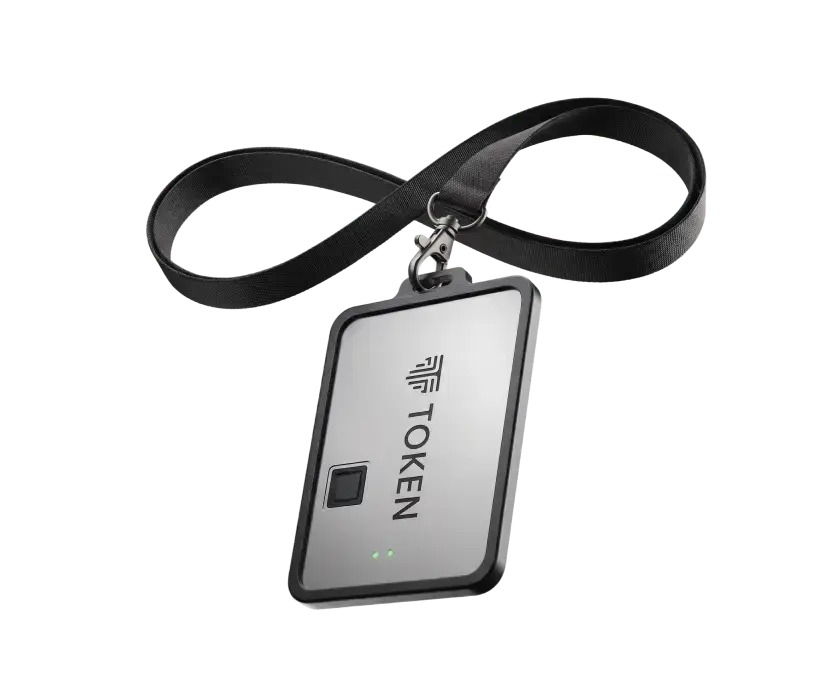
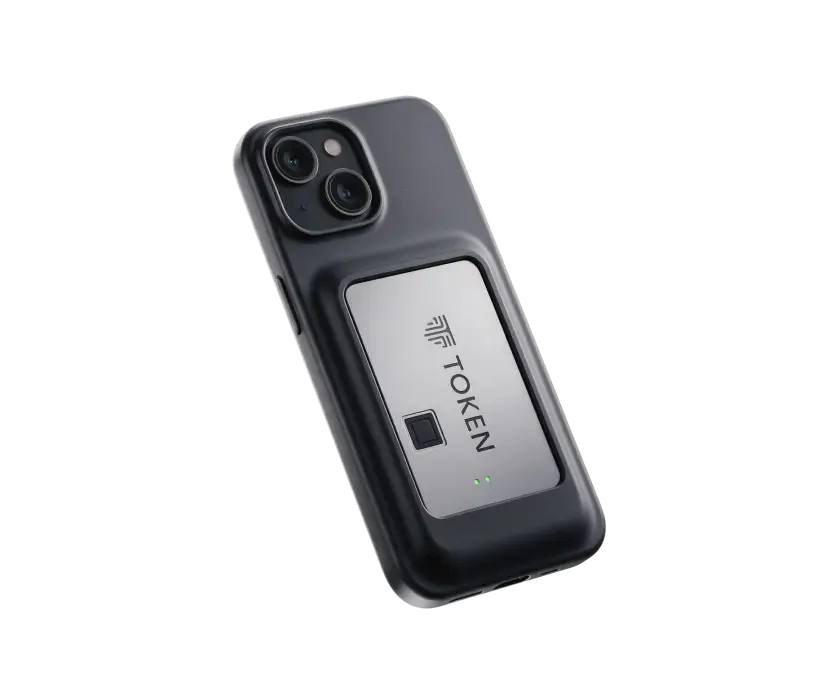
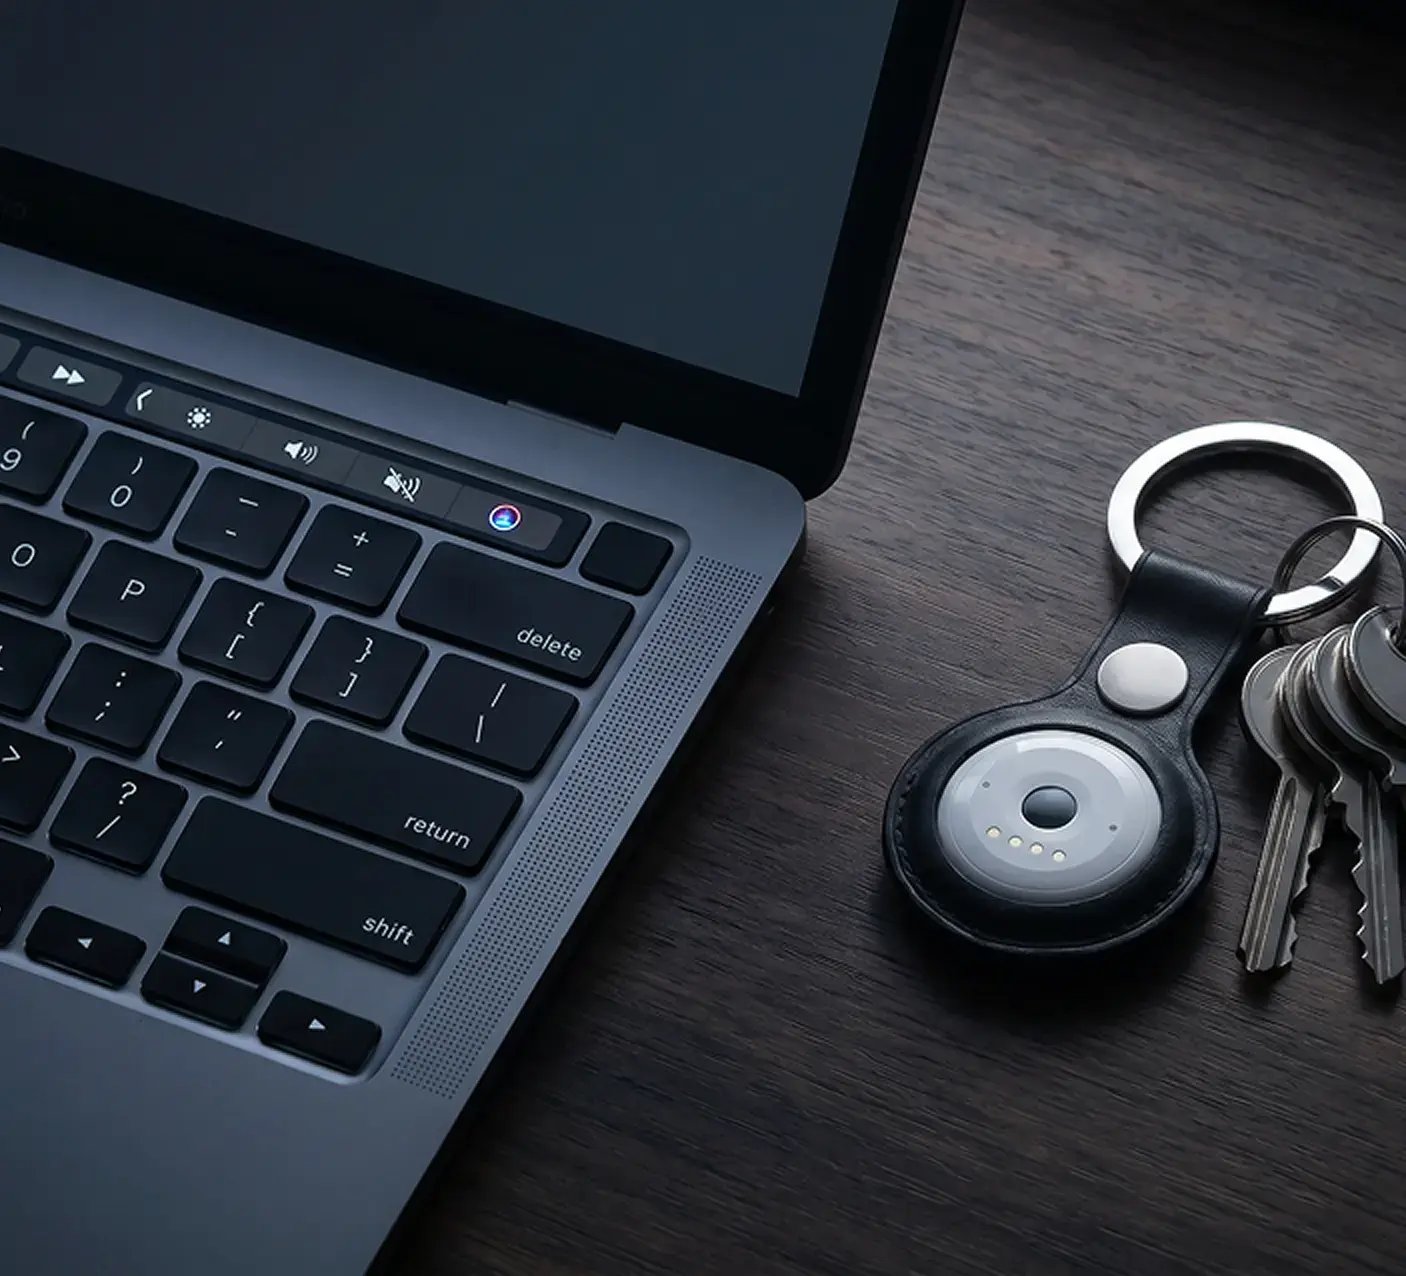
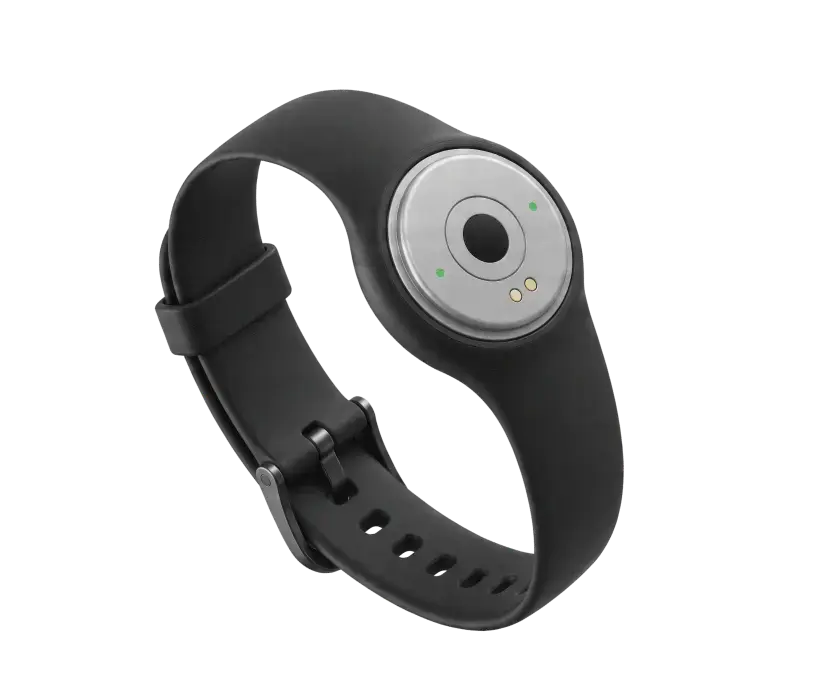
  • TokenCore™ Node in its silicone wrist band accessory

    Silicone Wrist Band

    TokenCore™
    Node

    Carried on a lanyard, wrist strap, key fob, or phone holder. The enterprise-scale anchor for shared floors and fast, deliberate verification.

    • Works with your existing SSO
    • Bluetooth 5.4
    • FIDO2 / WebAuthn
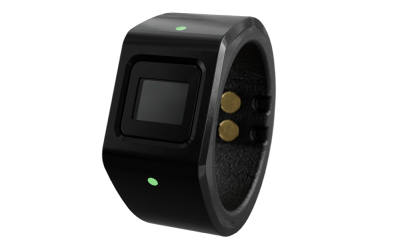
  • TokenCore™ Wearable biometric authenticator worn on the hand

    TokenCore™
    Wearable

    Identity assurance worn on the hand, so the authorized human is always the one present.

    • Works with your existing SSO
    • Bluetooth 5.4 & NFC
    • FIDO2 / WebAuthn
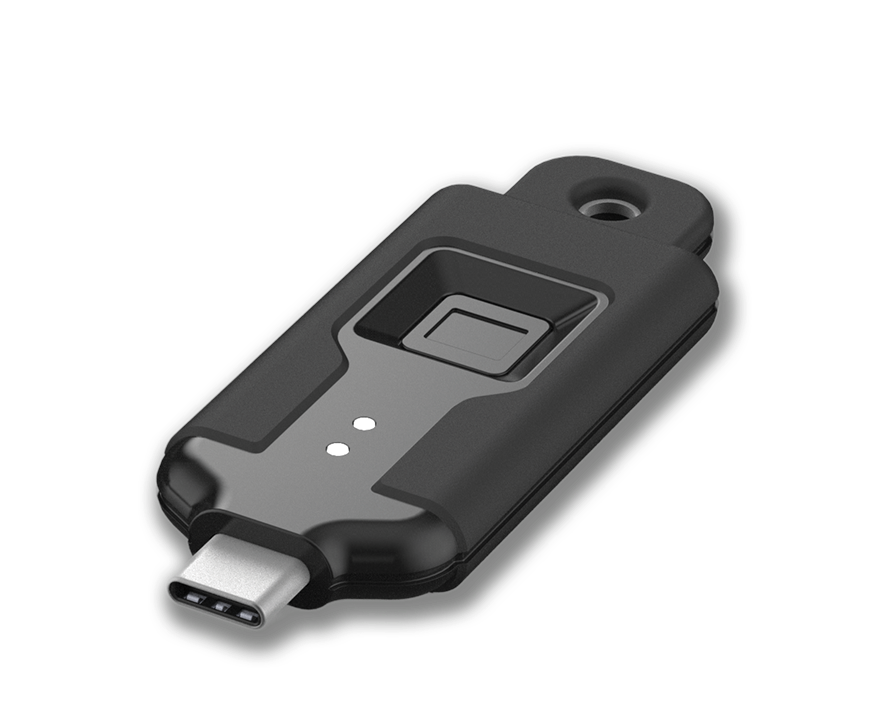
  • TokenCore™ Portable+ FIDO2 security key with fingerprint sensor and USB-C connector

    TokenCore™
    Portable+

    High-assurance authentication you carry. USB, Bluetooth, and NFC for mobile-first and mixed environments.

    • Works with your existing SSO
    • USB, Bluetooth 5.4 & NFC
    • FIDO2 / WebAuthn
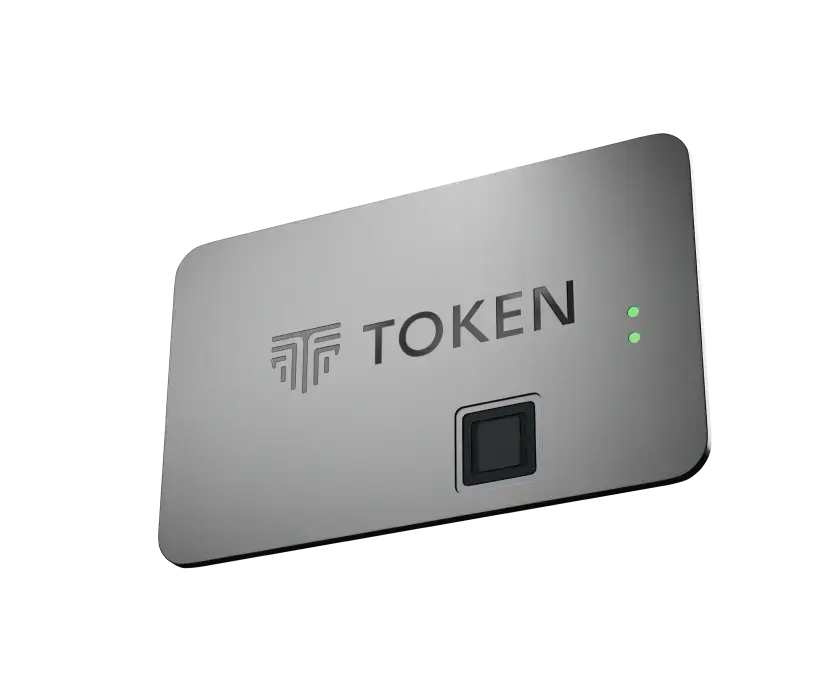
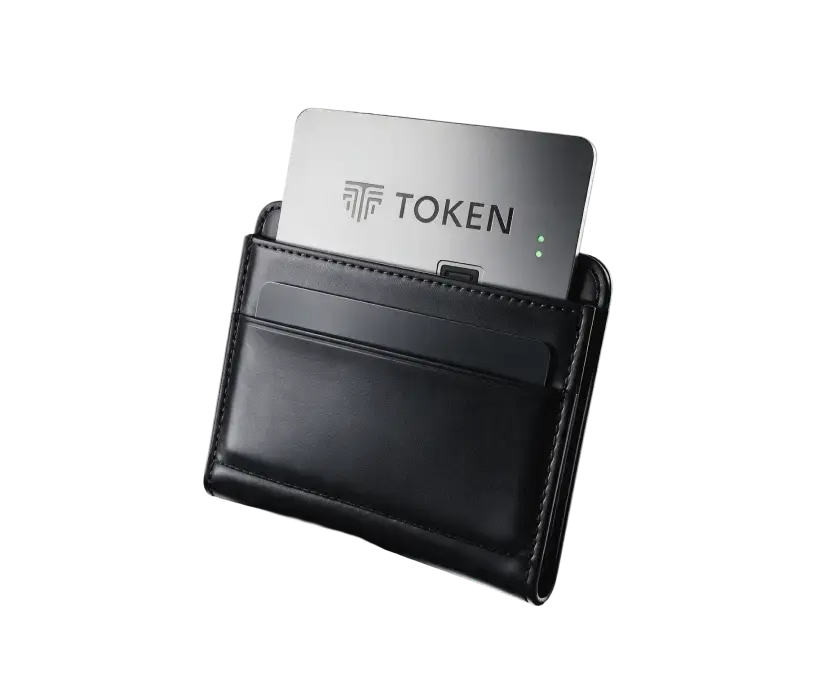
  • TokenCore™ Card, a metal keycard with a built-in fingerprint sensor

    Card Only

    TokenCore™
    Card

    The badge your people already carry, now a fingerprint-verified security key.

    • Works with your existing SSO
    • Bluetooth 5.4 & NFC
    • FIDO2 / WebAuthn

MFA Methods Compared

Which MFA Methods Can Be Phished?

Not all MFA is equal. Here's how each method holds up against phishing.

  1. 01

    SMS Code

    Phishable

    Fake sites relay the code in real time, and SIM swaps send it straight to the attacker.

  2. 02

    Authenticator App Code

    Phishable

    A fake login page asks for the 6-digit code and passes it on before it expires.

  3. 03

    Push / Number Matching

    Phishable

    Prompts get approved under pressure (MFA fatigue), and matching numbers can still be relayed.

  4. 04

    Passkey on a Phone

    Phishing-resistant

    Bound to the real website, but it proves the phone, not the person, and falls back to a PIN.

  5. 05

    TokenCore™

    Phishing-resistant + proves the person

    FIDO2 bound to the real website, plus a fingerprint matched on a dedicated device. No PIN fallback.

Of these, only the FIDO2 methods are phishing-resistant. TokenCore™ is FIDO2 plus a fingerprint check on a dedicated device.

How TokenCore™ Works

Three things have to be true before access is granted.

  1. Device Is Present.

    The TokenCore™ device has to be with the user: over Bluetooth 5.4 within about 3 ft, an NFC tap or USB-C. A remote attacker can't approve a login from somewhere else.

  2. Fingerprint Matches.

    The match happens on the device, inside a tamper-resistant chip certified to protect keys and biometric data. There's no PIN fallback: if the fingerprint doesn't match, nothing happens. See how fingerprint verification works.

  3. Login Is Signed.

    A FIDO2 credential signs the login, and it only works on the genuine website, so a fake site gets nothing it can reuse. Your fingerprint and keys never leave the device.

Compliance

Compliance Requirements

Regulators, insurers and platforms now ask for MFA that can't be phished. Here's where each one stands.

CISA and OMB M-22-09

Both call for phishing-resistant MFA, and CISA names FIDO2/WebAuthn as a widely available option. CISA's guidance explained.

PCI DSS v4.0.1

Requires MFA for all access into the cardholder data environment, set up so it can't be bypassed or replayed (Req. 8.4–8.5).

NYDFS Part 500

Section 500.12 requires MFA across remote and internal access to a covered entity's information systems.

HIPAA Security Rule

Requires covered entities to verify that a person seeking access to ePHI is who they claim to be.

CMMC

CMMC Level 2 requires MFA for privileged accounts, and for network access to non-privileged accounts.

FTC Safeguards Rule

Requires MFA for anyone accessing a covered financial institution's information systems.

Cyber Insurance

Insurers increasingly ask for phishing-resistant MFA on email, remote access and admin accounts.

Microsoft Entra and Salesforce

Entra Conditional Access can require phishing-resistant MFA, which TokenCore™ meets as a FIDO2 security key. Salesforce is moving admins and privileged users to it too.

No Phone Needed

Phishing-Resistant MFA Without a Mobile Phone

For phone-free areas like labs, secure sites and clinical floors, for frontline staff without a work phone, and for teams that won't put security apps on personal phones.

Node, Wearable and Card connect over Bluetooth or NFC. Portable plugs into USB-C. Nothing is installed on a personal phone.

govern-ai-actions
Identity Verified
  • Bluetooth 5.4
  • NFC tap
  • USB-C
Personal phone Nothing installed

Cyber Insurance

What Cyber Insurers Ask For

Cyber insurance applications now ask specific questions about MFA. Here's how TokenCore™ answers them.

Cyber insurance application

Multi-factor authentication

3 of 3 verified

  1. Question 1

    Do you enforce phishing-resistant MFA on email and remote access?

    Verified with TokenCore™

    How TokenCore™ answers it

    A FIDO2 security key with a fingerprint check, enforced in your identity provider.

  2. Question 2

    Is MFA required on all admin and privileged accounts?

    Verified with TokenCore™

    How TokenCore™ answers it

    Step-up with TokenCore™ through your PAM tool, such as CyberArk or Delinea.

  3. Question 3

    Have you removed SMS and push MFA for admins?

    Verified with TokenCore™

    How TokenCore™ answers it

    TokenCore™ replaces them for those users.

  • Works with what you have

    Okta, Microsoft Entra, Ping, Duo and CyberArk, as a FIDO2 security key, with no drivers or middleware. See what TokenCore™ works with.

  • Start where risk is highest

    Admins and finance approvers first, then everyone else.

  • Fast to roll out

    Under 90 seconds to enroll each user, and 30 days from pilot to rollout.

Teams

For Business Teams

Start with a pilot for your highest-risk users, then roll out to everyone else. Price per unit falls as the number rises, and our team prices larger orders.

Individuals

For Individuals

Phishing emails target personal accounts too. Add a TokenCore™ key to your Google, Microsoft, Apple ID, bank and crypto accounts that support security keys or passkeys. Buy direct, with next-business-day US shipping.

Industries

Phishing-Resistant MFA by Industry

FAQs

Frequently Asked Questions

Is push MFA phishing-resistant?

No. A fake site can trigger a real push prompt, and the user may approve it. Number matching helps against MFA fatigue, but it doesn't stop a real-time relay.

Is number matching enough?

No. It reduces MFA fatigue, but CISA doesn't class it as phishing-resistant, because the code can still be relayed. CISA treats it as a stopgap on the way to FIDO2.

Are passkeys phishing-resistant?

Yes. Passkeys use FIDO2, so they only work on the real website. But synced passkeys prove a device rather than the person, and they may fall back to a PIN.

Is FIDO2 phishing-resistant?

Yes. A FIDO2 credential only works on the genuine website's domain, so a fake site gets nothing it can use. TokenCore™ adds a fingerprint check on the device.

What does CISA say about SMS and authenticator apps?

CISA treats them as better than passwords alone, but not phishing-resistant, and recommends FIDO2. Read CISA's guidance explained.

Get Started

Make Identity Absolute

Get started with TokenCore™

Replace phishable MFA for the users who matter most, or protect your own accounts today.