The Authentication Architecture Problem

Wynn Resorts Breach: The Authentication Architecture Problem

Cybercriminals claiming affiliation with the ShinyHunters group have reportedly breached Wynn Resorts, demanding $1.5 million to prevent the release of stolen data. If accurate, the intrusion follows a pattern that has now repeated itself across hospitality, retail, insurance, and aviation. (Read the full article on Casino.org) The method is consistent. The attackers did not defeat network defenses. They authenticated.

Kevin Surace
2 minute read
Tycoon 2FA is down but the attack model is not

Tycoon 2FA Is Down. The Attack Model Is Not

Microsoft, Europol, Trend Micro, and a global coalition just disrupted Tycoon 2FA — one of the most prolific phishing-as-a-service platforms ever documented. That is a meaningful outcome. It is not safety. Tycoon 2FA is offline. The attack model that made it successful is not.

Kevin Surace
2 minute read

The Cybersecurity Industry Has a Terrifying Problem

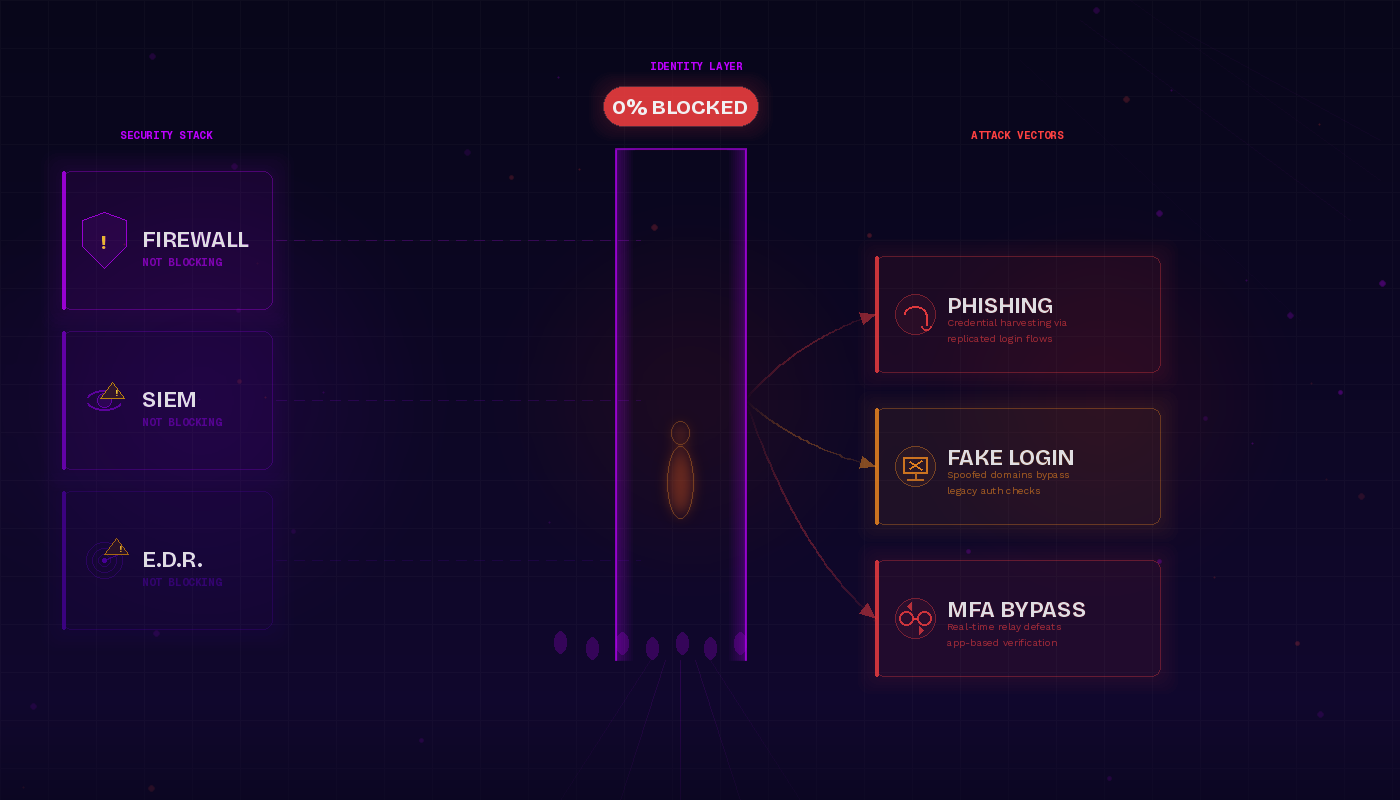
A new summary of the MITRE ATT&CK Enterprise Round 7 evaluation reveals that the highest protection score any tested vendor achieved was a mere 31 percent — meaning that 69% of attacks went entirely undetected by even the best-performing vendor in the field. But the more significant finding was buried beneath that number. Across every identity-specific attack scenario in the evaluation, all vendors scored zero blocking — not partial detection, not near misses, but zero. The tools enterprises invest in to stop modern attacks did not intercept a single identity attack, which is precisely the class of threat that now defines the modern threat landscape.

Kevin Surace
4 minute read
1 2 3 4

Stay Identity Assured

Subscribe to The Assured Identity Brief for sharp insights on identity security, authentication, and the threats security leaders must stay ahead of.