Device-Bound Security
Absolute Identity Assurance
Biometric authentication devices and human-bound passkeys for the enterprise
TokenCore™ combines biometric verification and dedicated security hardware to prove the authorized person is actually the person accessing your system, or approving what an AI agent does.
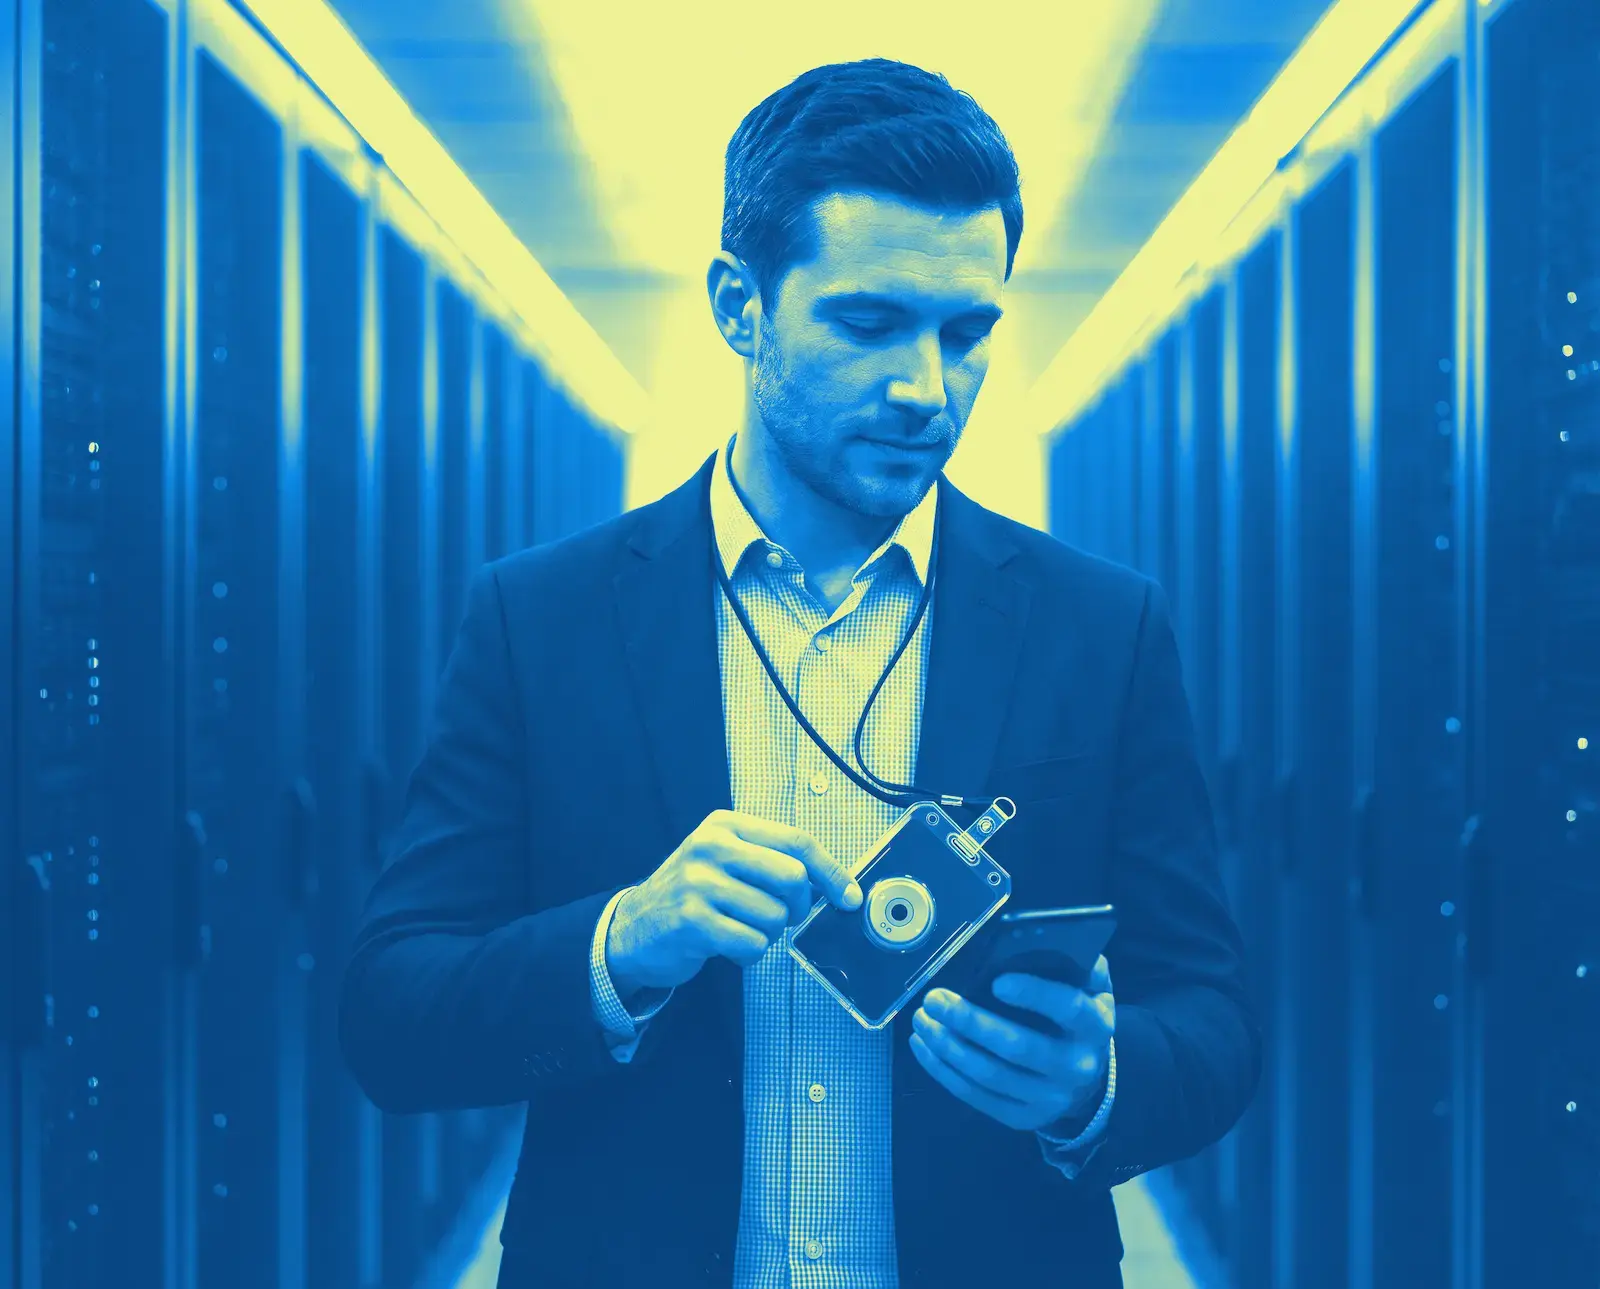
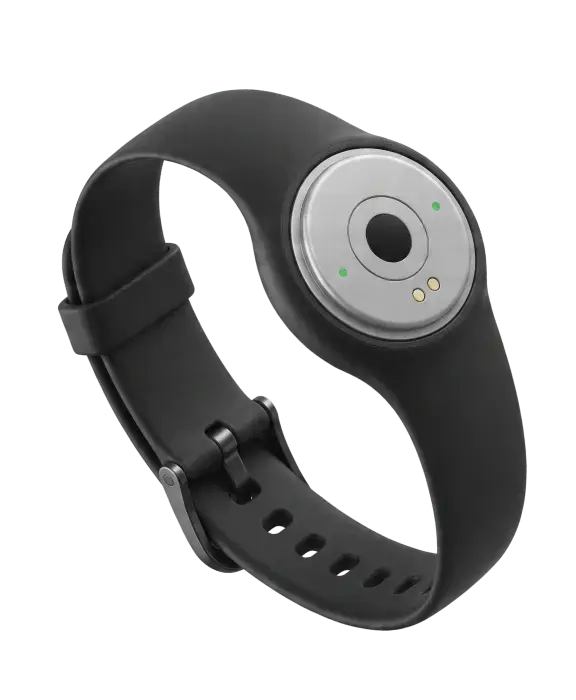
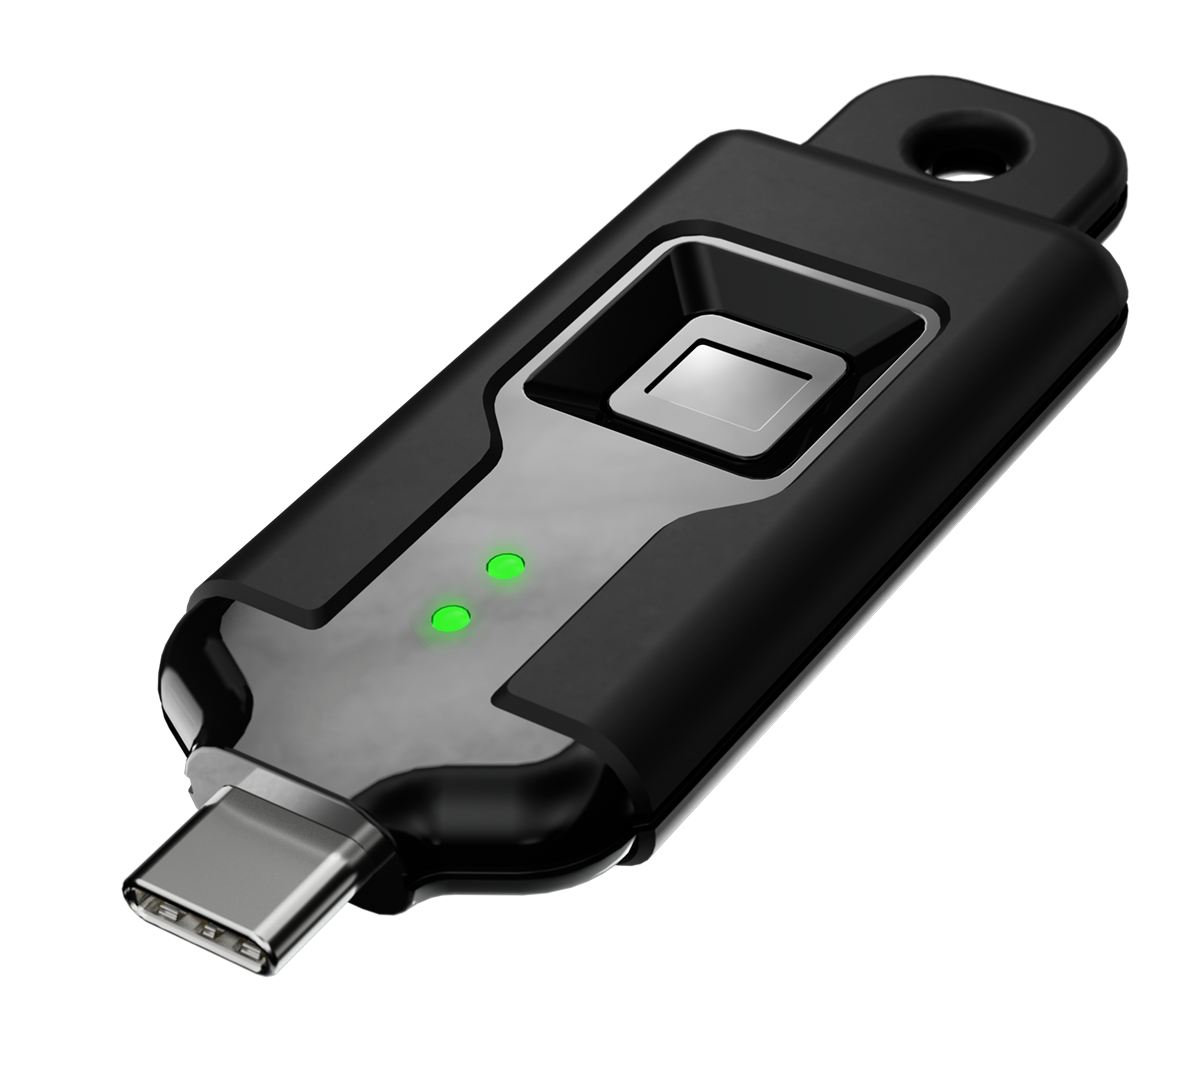
TokenCore™ Node
FIDO2 • Biometric • Passwordless
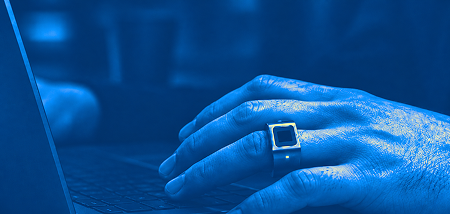
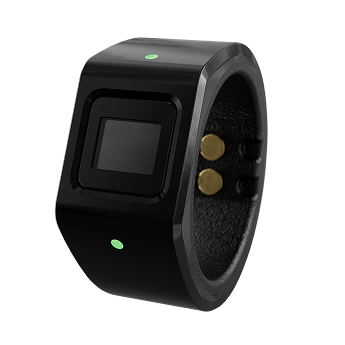
For Humans and AI Agents
The same human assurance protects the people accessing your systems and the consequential actions initiated by AI agents.
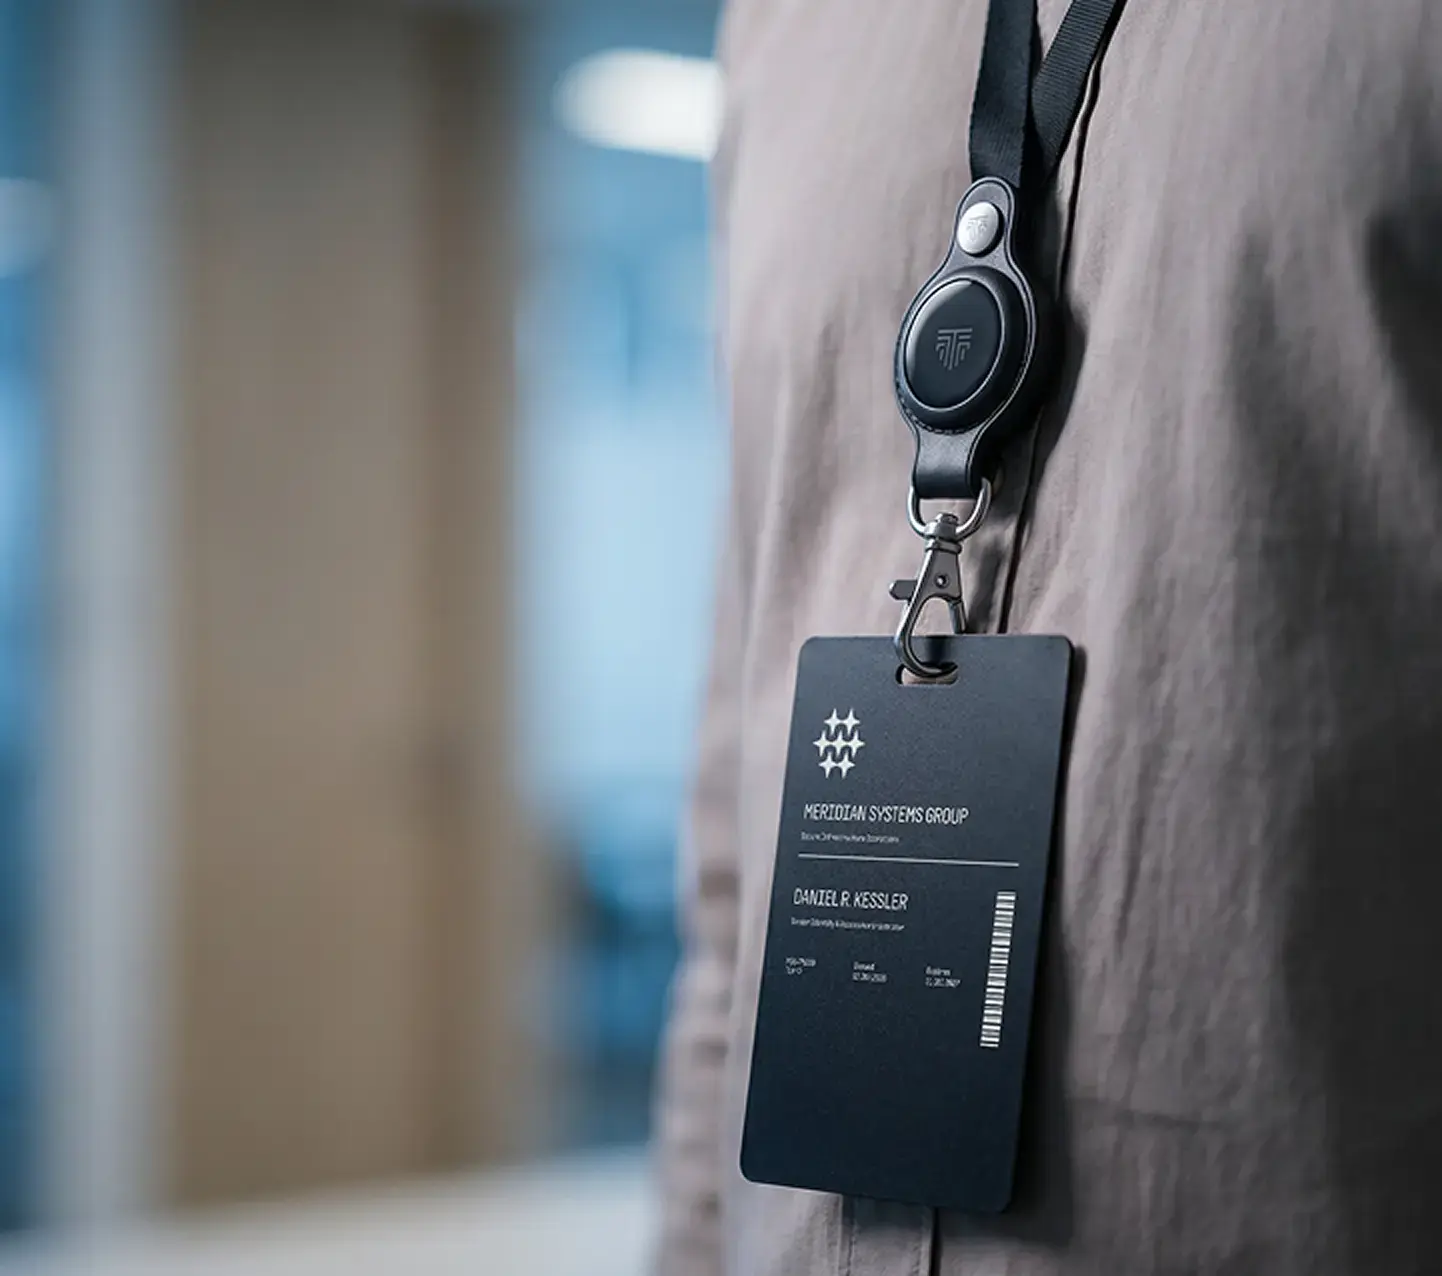
Humans
Protect Human Access
Prove the authorized individual is behind the access.
J. Reyes
Applications
- Employee Access Verified
- Privileged Access Verified
- Sensitive Systems Verified
- High-Consequence Transactions Verified
- Enrollment & Recovery Verified
AI Agents
Govern AI Actions
Put a verified human at the point of consequence.
Treasury Agent
Action Request
Release wire transfer
$250,000.00
To vendor account ending 4821. Prepared by AI agent.
An AI agent can prepare the $250,000 transfer. TokenCore™ proves the authorized human approved releasing it.
When an agentic workflow crosses a threshold that matters, TokenCore™ is the deterministic human-in-the-loop.
Human-Bound Passkeys
Not All Passkeys Are Created Equal.
Every passkey proves something. The question is what, now that AI agents act on a person's behalf.
Standard Passkey
Proves possession of a credential.
- Credential Valid
- Device Unlocked
- Person Not verified
Evolves Over the Air
Most security keys are fixed the day they ship. When the technology moves on, the fleet gets replaced, one enrollment at a time. TokenCore™ updates over the air, with no recall and no added load on your help desk.
Exclusive to One Human
A lightweight device that only one enrolled person can activate. Bluetooth and NFC proximity mean authentication requires physical presence at the workstation.
Whitepaper
Passkeys Are Not Completely Secure After All, Unless They Are Tied to Dedicated Biometric Hardware
Works With Your Stack
Keep What Works.
Works with your existing SSO on day one. No rip and replace. Add TokenCore™ where identity requires higher assurance.
Seamless interoperability with Microsoft Entra, Okta, Ping, Duo, PAM systems, and AI agent gateways. You made the right investment. TokenCore™ completes it.
Deployment Guide
Locking Microsoft Entra to Token Hardware Bound Biometric Authentication
Download the Guide


How It Works
Three Things Must Be True.
Strip away the terminology. A login, or an AI agent's action, goes ahead when all three are true, and not before.
-
01
The Device Is There.
TokenCore™ hardware must be present.
Searching Verified -
02
The Human Is There.
Their fingerprint must match.
Identity Verified -
03
The System Knows Both Are True.
Cryptography proves the authentication to the application.
 Verifying Verified
The Evolution of Authentication
Every Generation Solves Yesterday's Weakness. New Threats Expose the Next Gap.
Passwords weren't enough. MFA wasn't enough. Passkeys improved the equation. But access is still not the same thing as identity, and AI agents now act on credentials alone.
TokenCore™ is built for tomorrow's threats.
Passwords
Something you know.
What It Proves
Someone knows the secret.
The Gap It Left
Anything known can be shared, guessed, reused, or phished.
Legacy MFA
Something else you receive.
What It Proves
Someone received a code or a push notification.
The Gap It Left
Codes get intercepted. Push prompts get approved by whoever is holding the phone.
Modern MFA
Something on your phone.
What It Proves
An enrolled app approved the request.
The Gap It Left
Real-time phishing relays the approval. The phone proves the device, not the person holding it.
Passkeys
Something you possess.
What It Proves
A cryptographic credential, bound to the real site. Phishing-resistant by design.
The Gap It Left
Synced passkeys travel between devices. The credential proves possession, not the person.
Biometric Authentication
Something you are, on a shared device.
What It Proves
A face or fingerprint unlocked the phone or laptop.
The Gap It Left
A PIN fallback sits behind the biometric, and the device isn't bound to one human.
TokenCore™
Something you possess and only you can activate.
What It Proves
The enrolled human is present. Their fingerprint is matched on dedicated hardware before a hardware-bound FIDO2 credential signs.
The Gap It Closes
No PIN fallback. Nothing to sync. No delegation.
- Passwords: Something you know. What it proves: Someone knows the secret. The gap it left: Anything known can be shared, guessed, reused, or phished.
- Legacy MFA: Something else you receive. What it proves: Someone received a code or a push notification. The gap it left: Codes get intercepted. Push prompts get approved by whoever is holding the phone.
- Modern MFA: Something on your phone. What it proves: An enrolled app approved the request. The gap it left: Real-time phishing relays the approval. The phone proves the device, not the person holding it.
- Passkeys: Something you possess. What it proves: A cryptographic credential, bound to the real site. Phishing-resistant by design. The gap it left: Synced passkeys travel between devices. The credential proves possession, not the person.
- Biometric Authentication: Something you are, on a shared device. What it proves: A face or fingerprint unlocked the phone or laptop. The gap it left: A PIN fallback sits behind the biometric, and the device isn't bound to one human.
- TokenCore™: Something you possess and only you can activate. What it proves: The enrolled human is present. Their fingerprint is matched on dedicated hardware before a hardware-bound FIDO2 credential signs. The gap it closes: No PIN fallback. Nothing to sync. No delegation.
Why TokenCore™
More Than a Security Key
A security key proves possession. TokenCore™ combines six properties that prove the person, behind every login and every AI agent action.
See the Full Comparison-
Biometric Authentication
Your fingerprint, and only your fingerprint, activates the credential.
-
Hardware-Bound
The credential stays tied to dedicated hardware at all times.
-
Proximity
The authenticator must be physically present where required.
-
Cryptographic
The legitimate service is verified before authentication occurs.
-
Upgradeable
Security evolves without replacing an enterprise fleet of devices.
-
Enterprise-Controlled
Your organization controls enrollment, authentication policies, and recovery.
One Assurance Platform
Built for the Way Your Workforce Works
Biometric authentication devices and hardware passkeys
Pick the form factor that fits the role. Every one enforces fingerprint verification, keeps the credential on the hardware, and speaks FIDO2. The same fingerprint that signs a person in also approves their AI agents' actions.
-
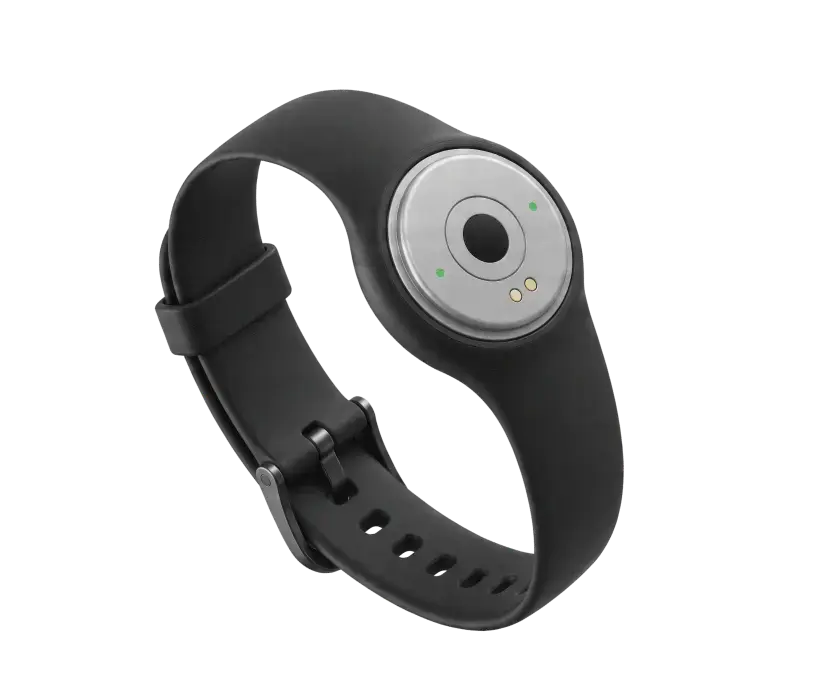
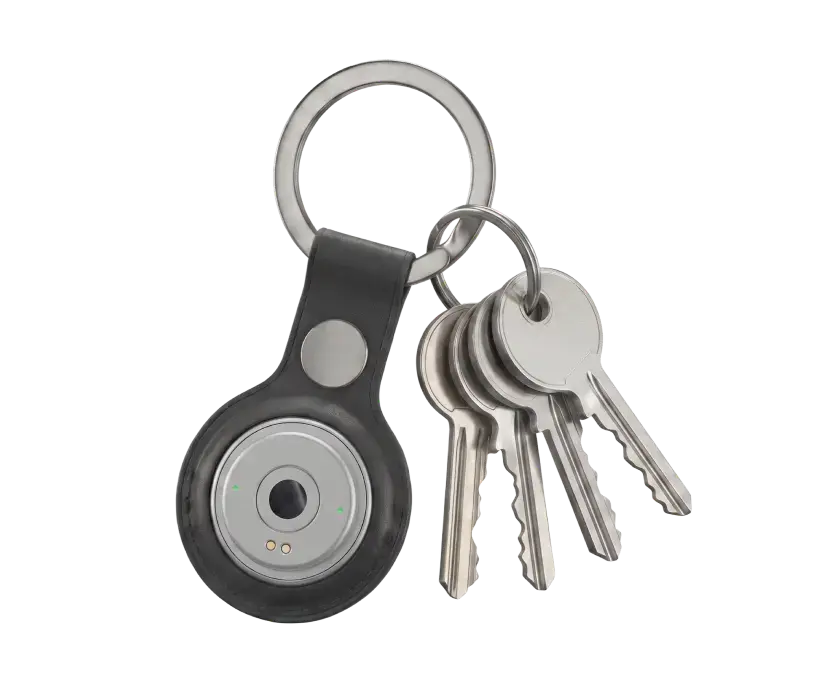
Silicone Wrist BandKey FobLanyardReelPhone MountID Badge
TokenCore™
NodeCarried on a lanyard, wrist strap, key fob, or phone holder. The enterprise-scale anchor for shared floors and fast, deliberate verification.
- Works with your existing SSO
- Bluetooth 5.4
- FIDO2 / WebAuthn
-
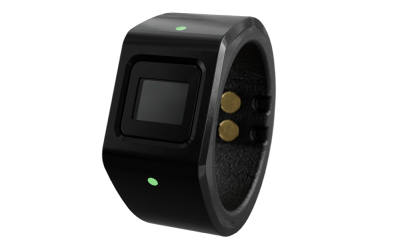
TokenCore™
WearableIdentity assurance worn on the hand, so the authorized human is always the one present.
- Works with your existing SSO
- Bluetooth 5.4 & NFC
- FIDO2 / WebAuthn
-
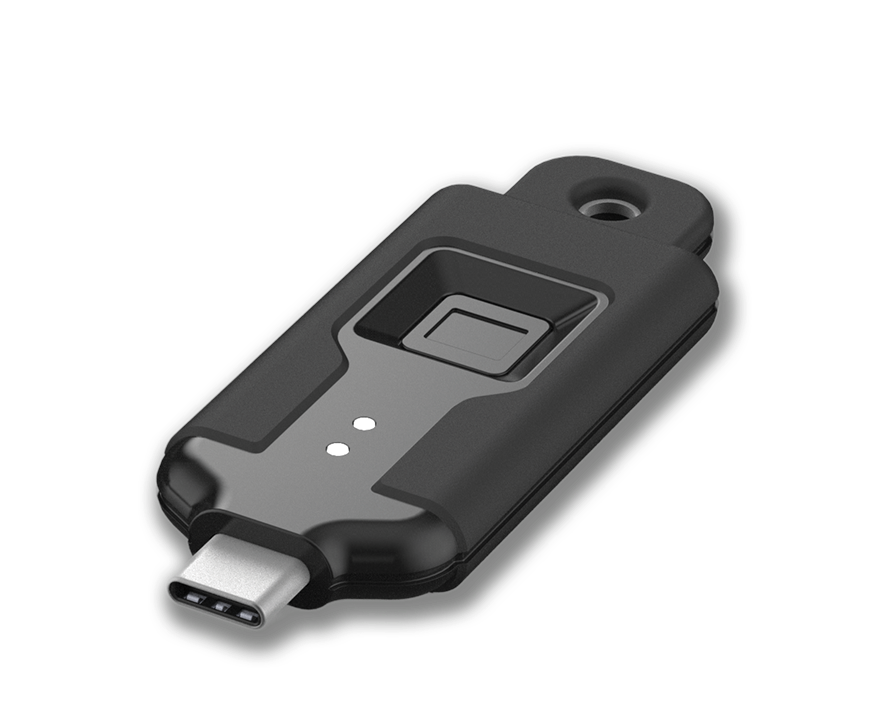
TokenCore™
Portable+High-assurance authentication you carry. USB, Bluetooth, and NFC for mobile-first and mixed environments.
- Works with your existing SSO
- USB, Bluetooth 5.4 & NFC
- FIDO2 / WebAuthn
-
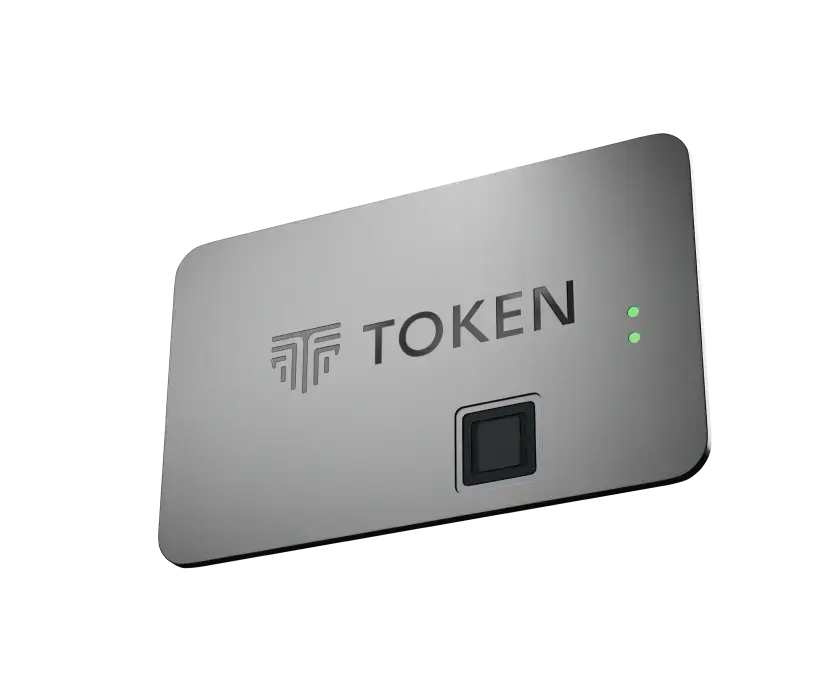
Card OnlyID BadgeLanyardPhone WalletWallet
TokenCore™
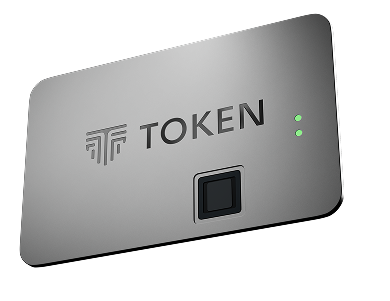
CardElevates the everyday keycard to verify who is actually gaining access.
- Works with your existing SSO
- Bluetooth 5.4 & NFC
- FIDO2 / WebAuthn
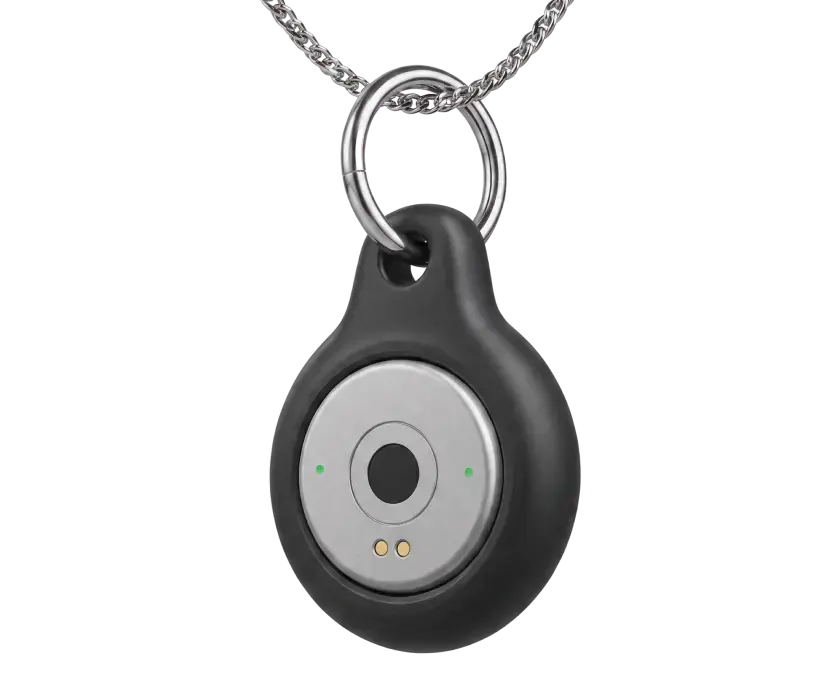
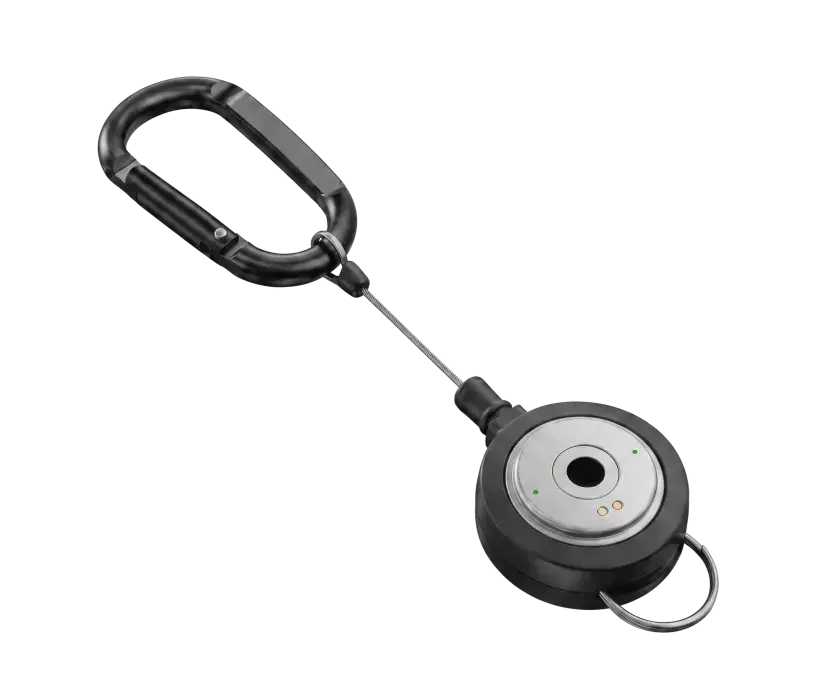
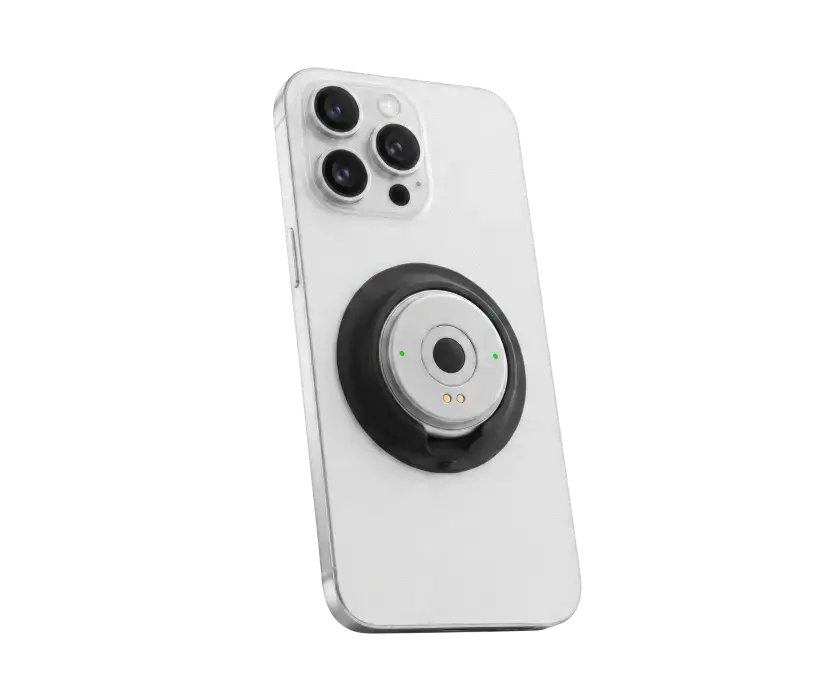
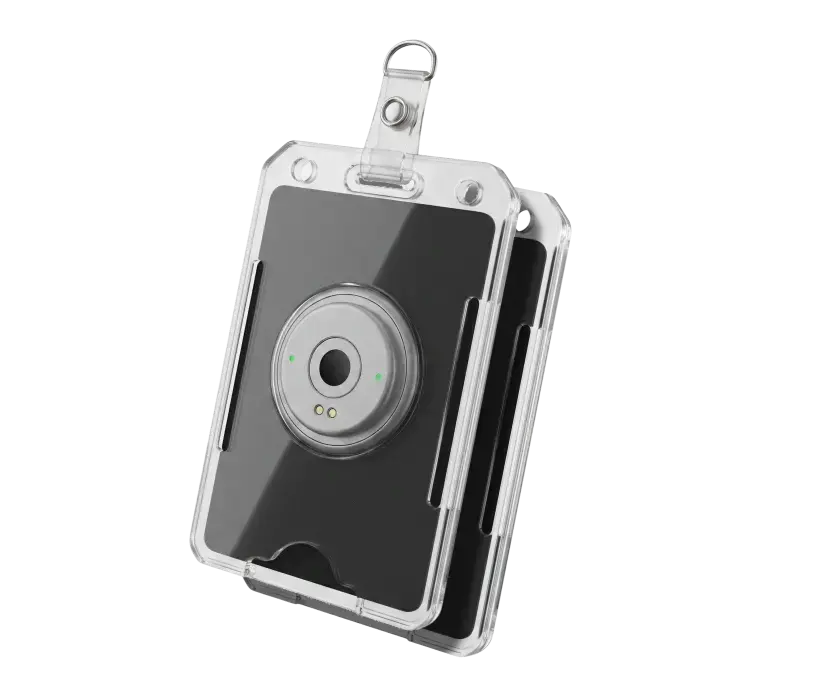
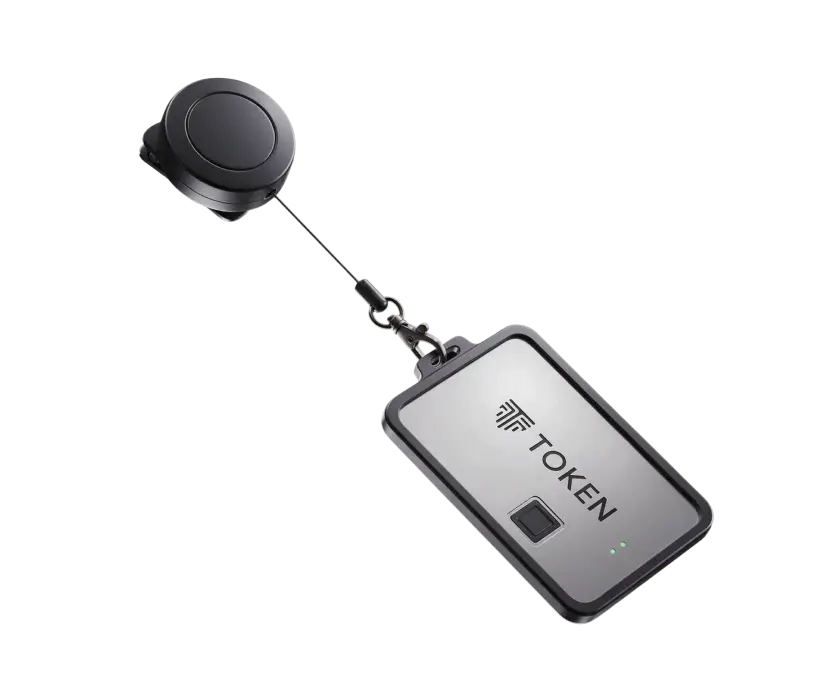
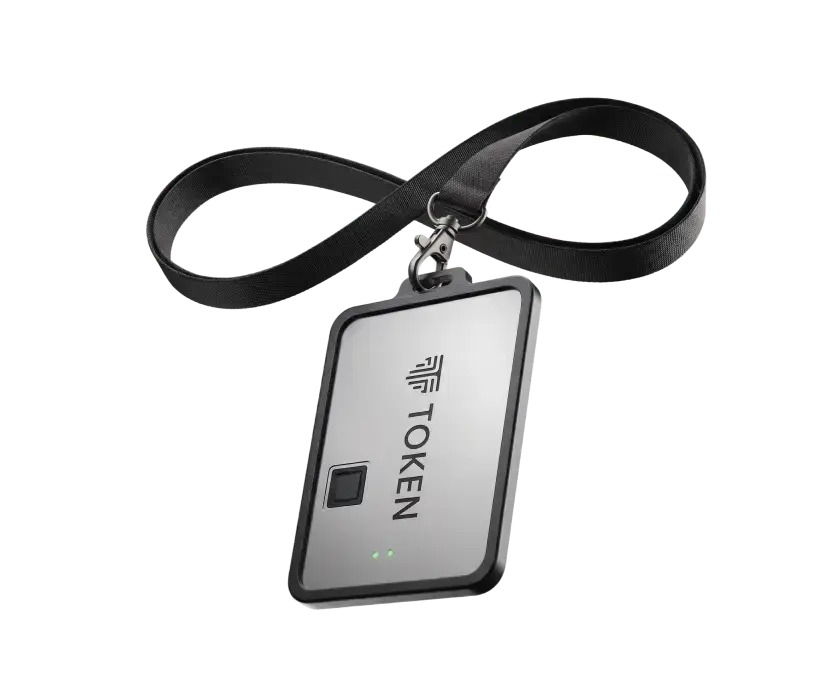
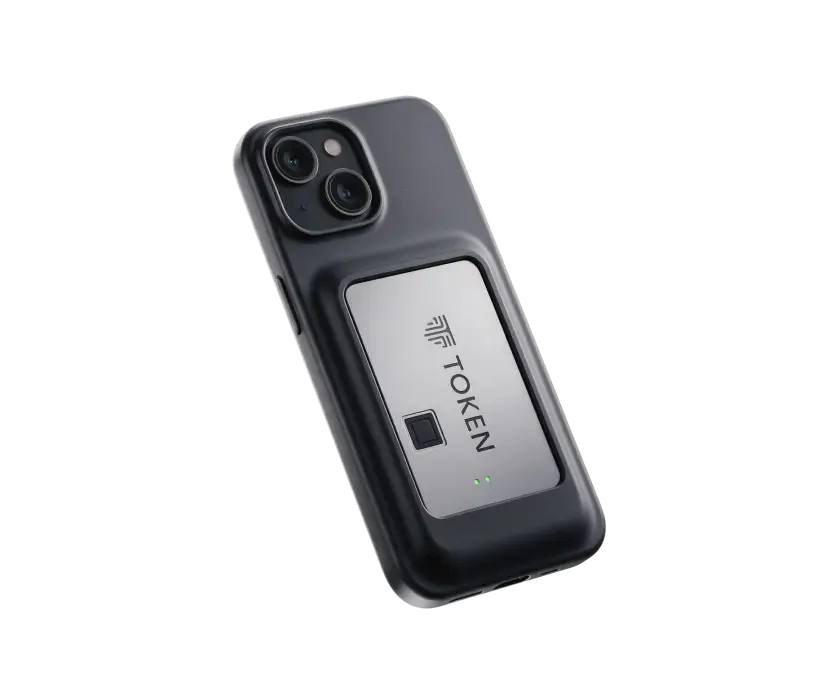
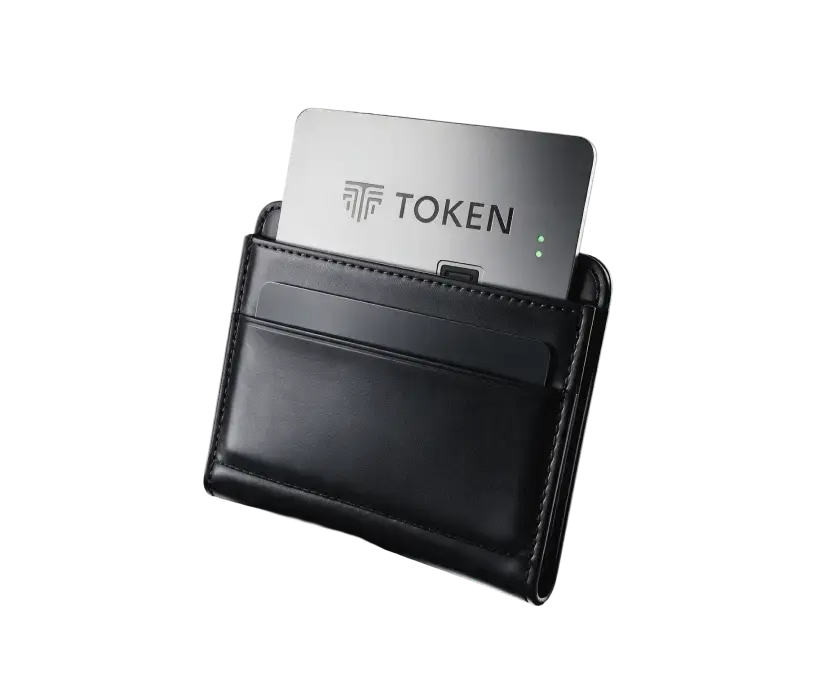
Buy direct from the TokenCore™ store, or talk to us about volume pricing for enterprise rollouts.
The Trust Lifecycle
Identity Risk Doesn't Begin and End at Login.
TokenCore™ doesn't simply add a fingerprint to login. Organizations need protection beyond it: through enrollment, loss and recovery, resets, updates, rollouts, and the actions AI agents take.
Stage 01 / 07
Enroll
Who enrolled the credential?
Where Identity Fails
A credential is only as trustworthy as its enrollment. Attackers don't break passkeys. They enroll new ones.
Where TokenCore™ Fits
Enrollment is enterprise-controlled. The fingerprint is registered on TokenCore™ hardware and the credential is created there, bound to one human.
Stage 02 / 07
Authenticate
Who is actually signing in?
Where Identity Fails
Passwords, codes, and synced passkeys prove possession, not presence.
Where TokenCore™ Fits
A live fingerprint match on-device, with the authenticator physically present, before the credential signs. No PIN fallback.
Stage 03 / 07
Elevate
Who is elevating privilege?
Who approved the consequential action?
Where Identity Fails
Admin rights and consequential actions ride on trust from a login that happened earlier, often hours earlier.
Where TokenCore™ Fits
Step-up verification at the moment of elevation. The same fingerprint gates privileged actions and approvals, including those initiated by AI agents.
Stage 04 / 07
Recover
Who is requesting recovery?
Who is calling the help desk?
Where Identity Fails
Recovery runs on assumptions. A convincing caller can talk their way into a reset.
Where TokenCore™ Fits
Recovery stays enterprise-controlled and ties back to the enrolled human, not to a voice on the phone.
Stage 05 / 07
Replace
Who receives the replacement?
Where Identity Fails
A lost or broken authenticator forces re-enrollment. Every re-enrollment is another chance to enroll the wrong person.
Where TokenCore™ Fits
Replacement runs through the same enterprise-controlled enrollment, bound to the same verified human.
Stage 06 / 07
Update
How do devices stay current?
Where Identity Fails
Fixed hardware ages in place. Upgrading means replacing the fleet and re-enrolling everyone on it.
Where TokenCore™ Fits
Signed firmware updates over the air. Deployed units gain new capability instead of being replaced.
Stage 07 / 07
Revoke
Who still has access?
Where Identity Fails
Departures and lost devices leave working credentials behind until someone removes them.
Where TokenCore™ Fits
The credential lives on one device, bound to one human. Revoke it in your identity provider and that access ends.
High-Security Industries
Don't Leave Security to Chance.
TokenCore™ adds biometrically assured identity wherever the person behind the access matters as much as the credential itself. Even more so for privileged access users and the AI agents acting for them.
-
-
-
-
Critical Infrastructure
Compliance
-
Insurance
Compliance
Compliance Standards
See how TokenCore™ maps to your framework's authentication requirements.
Business Outcomes
What Becomes Possible with TokenCore™
Make Identity Absolute
Whether access begins with a person or an AI agent, consequential actions should end with verified human identity.
Ready to deploy? Buy Now