Kevin Surace
2 minute read
Insurance carriers are not being targeted because their security teams have failed. They are being targeted because their operating model exposes identity at scale, and attackers know exactly where that exposure sits.
Modern insurers manage high volumes of regulated personal and financial data across distributed workforces, third-party administrators, and outsourced service centers. Identity crosses organizational boundaries constantly. Every handoff is a potential entry point.
Recent attacks on insurance firms follow a consistent pattern. The intrusion does not begin with malware or a vulnerability exploit. It begins with impersonation. An attacker presents as an employee or contractor. They invoke a support process. MFA is reset. Access is granted.
This is not a failure of perimeter security. It is a failure of identity architecture.
Push notifications, authenticator apps, and even passkeys share a critical assumption: that the person enrolling is the person they claim to be. In a heavily outsourced environment—where employees are onboarded remotely, access is managed across organizational boundaries, and support desks operate under pressure—that assumption cannot hold.
When identity can be re-issued through a phone call or a ticketing system, attackers do not need to circumvent controls. They simply request access through the process designed to grant it.
Token removes remote identity issuance from the equation entirely. Authentication is bound to a physical Token device issued to a specific individual. Every authentication event requires biometric verification and physical possession. There is no credential to steal. There is no enrollment flow an attacker can abuse remotely.
A support agent cannot enroll a new Token on behalf of someone else. A process override cannot bypass the biometric requirement. Identity does not travel over a phone call.
Insurance underwriters and regulators are shifting their focus from perimeter defenses to identity controls. Legacy MFA is no longer treated as a strong signal—particularly when it remains resettable through administrative processes.
Token provides what insurers currently struggle to demonstrate: verifiable proof that identity cannot be re-issued remotely, that credentials do not exist to be stolen, and that every authentication event is tied to a specific individual’s physical presence and biometric confirmation.
Organizations enforcing hardware-bound, biometrically-verified identity are positioned to demonstrate measurably stronger controls as underwriting standards evolve. Organizations relying on resettable MFA are not.
Attackers have already adapted to the current reality. They target environments where identity is weakest—where it can be transferred, reset, or socially engineered. Insurance, with its distributed workforce and trust-dependent support processes, presents exactly that profile.
Token hardens identity in alignment with how modern attacks actually operate. Not how frameworks once assumed they would.
Ransomware does not start with ransomware. It starts with access. An attacker who can log in as a legitimate user can move quietly through the network, escalate their privileges and deploy a payload before anyone notices. Most ransomware defences focus on the payload stage. The attackers win before that stage is even reached. The ransomware kill chain is a framework for understanding how attacks progress from first contact to full compromise. Breaking it requires understanding where in the chain authentication failures occur and what it would take to close them.
A new report from CyberCube just confirmed what many of us in cybersecurity have long suspected: Scattered Spider is targeting hundreds of major enterprises with precision. Nearly 300 companies—each with over $500 million in annual revenue—have been flagged as high-risk. Why? Because they’re still running the same legacy technologies this threat group exploits with shocking ease.
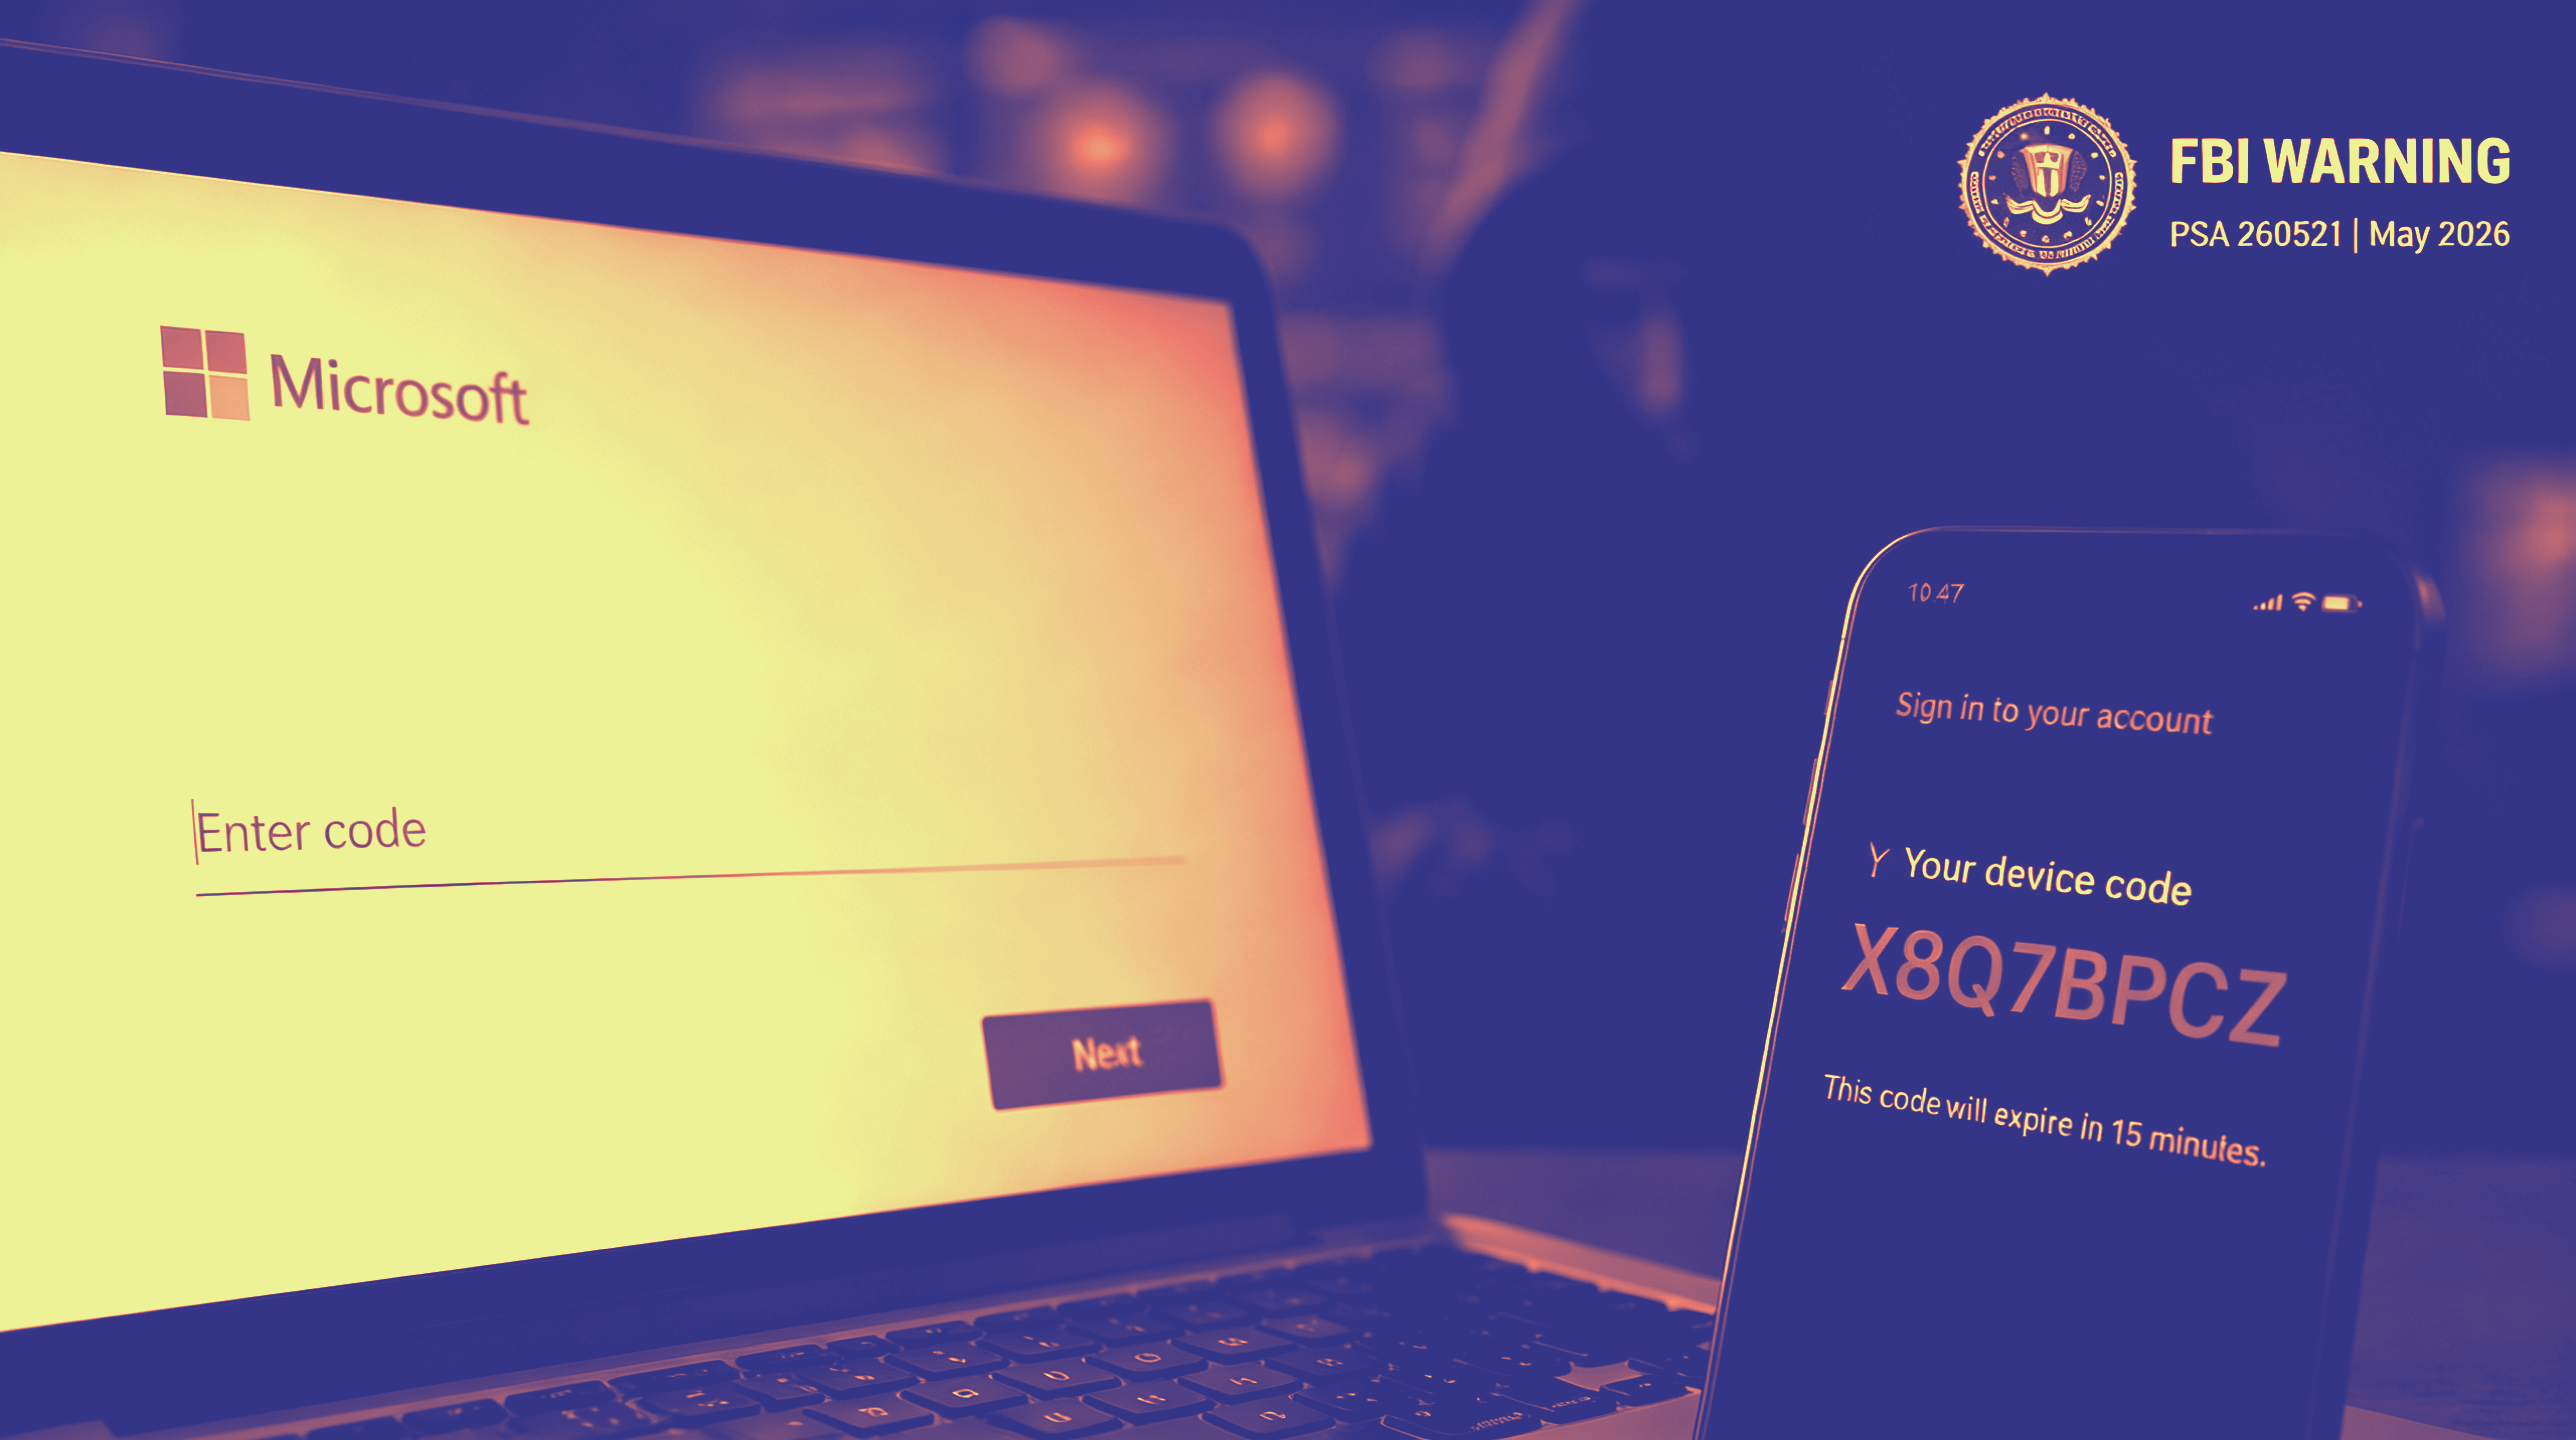
Here’s How Enterprises Using TokenCore Devices Should Respond. The FBI and CISA recently issued a public warning about a rapidly growing attack technique abusing Microsoft 365 "device code flow" authentication. The advisory explains how attackers are using legitimate OAuth authorization workflows to gain persistent access to enterprise Microsoft 365 environments without stealing passwords or bypassing MFA in the traditional sense. This is an important moment for the industry because it highlights a larger truth: Strong authentication alone is no longer enough.
Subscribe to The Assured Identity Brief for sharp insights on identity security, authentication, and the threats security leaders must stay ahead of.